Semgrep
Service Overview
Section titled “Service Overview”Semgrep is an intelligent code analysis and security scanning service that empowers software developers and security teams to identify and remediate code vulnerabilities efficiently. With its advanced pattern-based approach, Semgrep helps organizations proactively detect security issues, compliance violations, and other code quality concerns throughout the software development lifecycle.
Key Features
Section titled “Key Features”- Pattern-based Code Scanning: Semgrep uses a powerful pattern-matching engine to analyze source code and identify potential security flaws, coding errors, and adherence to best practices. It supports multiple programming languages, making it versatile for diverse software projects.
- Custom Rule Creation: The service allows users to create custom rules to tailor code scanning to their specific security and coding standards. This flexibility ensures a comprehensive analysis of codebases according to unique project requirements.
- Continuous Integration (CI) Integration: Semgrep seamlessly integrates with popular CI/CD platforms, enabling automatic code scanning during the development process. Developers receive real-time feedback on issues, promoting early bug detection and faster remediation.
- Security and Compliance Rule Sets: Semgrep includes a comprehensive library of security and compliance rule sets developed by industry experts and the open-source community. These rule sets align with best practices, security standards, and regulatory frameworks.
- Extensive Language Support: The service supports a wide range of programming languages, including but not limited to Python, JavaScript, Java, C/C++, and Go, making it suitable for diverse software stacks.
Key Benefits
Section titled “Key Benefits”- Early Bug Detection: By analyzing code as it is written, Semgrep helps catch bugs and security issues early in the development process, reducing the time and effort required for later bug fixing.
- Customizable and Adaptable: With the ability to create custom rules and apply various rule sets, organizations can align Semgrep’s scanning capabilities with their specific security policies and coding conventions.
- Continuous Security Feedback: The seamless integration with CI/CD pipelines provides developers with immediate feedback, fostering a security-conscious development culture and reducing time-to-fix for vulnerabilities.
- Comprehensive Security Scanning: Semgrep’s extensive language support and diverse rule sets ensure a thorough examination of codebases, addressing various security concerns and compliance requirements.
- Open Source Community: Semgrep is built on an open-source foundation, actively maintained by a large and engaged community, providing access to continuously updated rules and enhancements.
Semgrep is an indispensable tool for organizations committed to building secure and reliable software applications, enhancing overall code quality, and reducing security risks.
Getting Started with Semgrep
Section titled “Getting Started with Semgrep”-
Go to https://semgrep.dev/orgs/-/settings/tokens, and click on the
Create new tokenbutton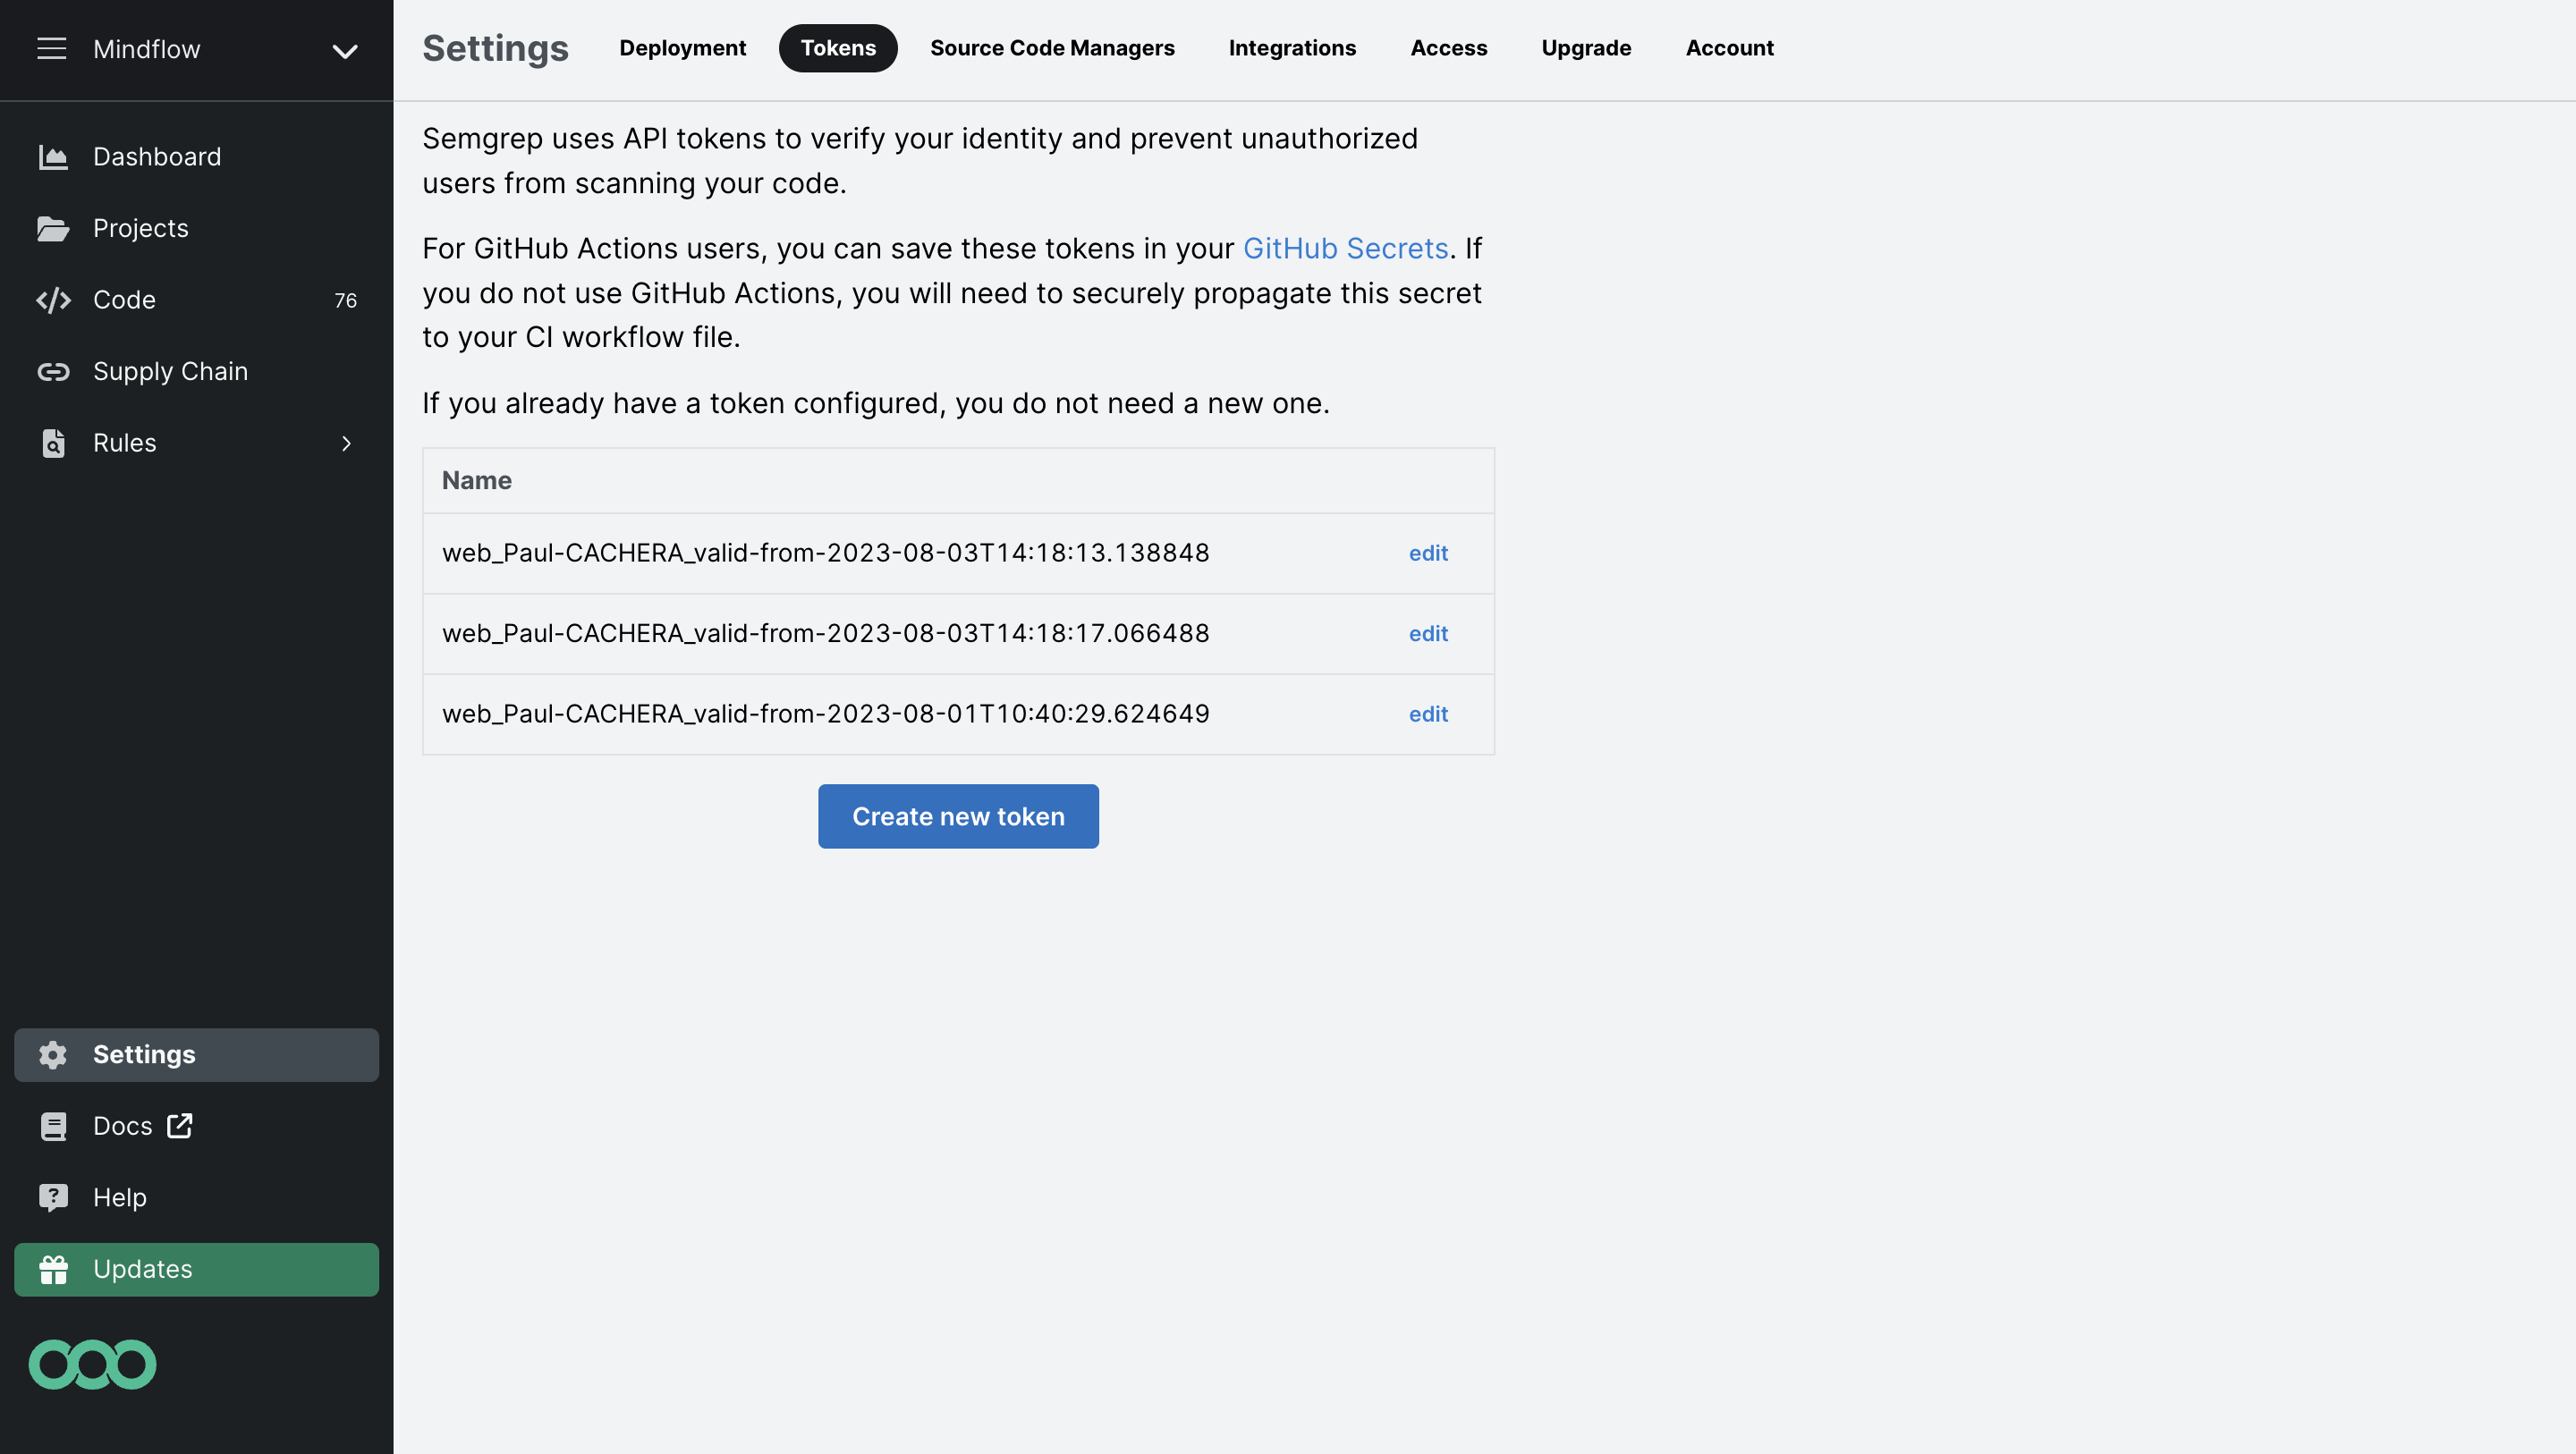
-
Copy the token and click on the
updatebutton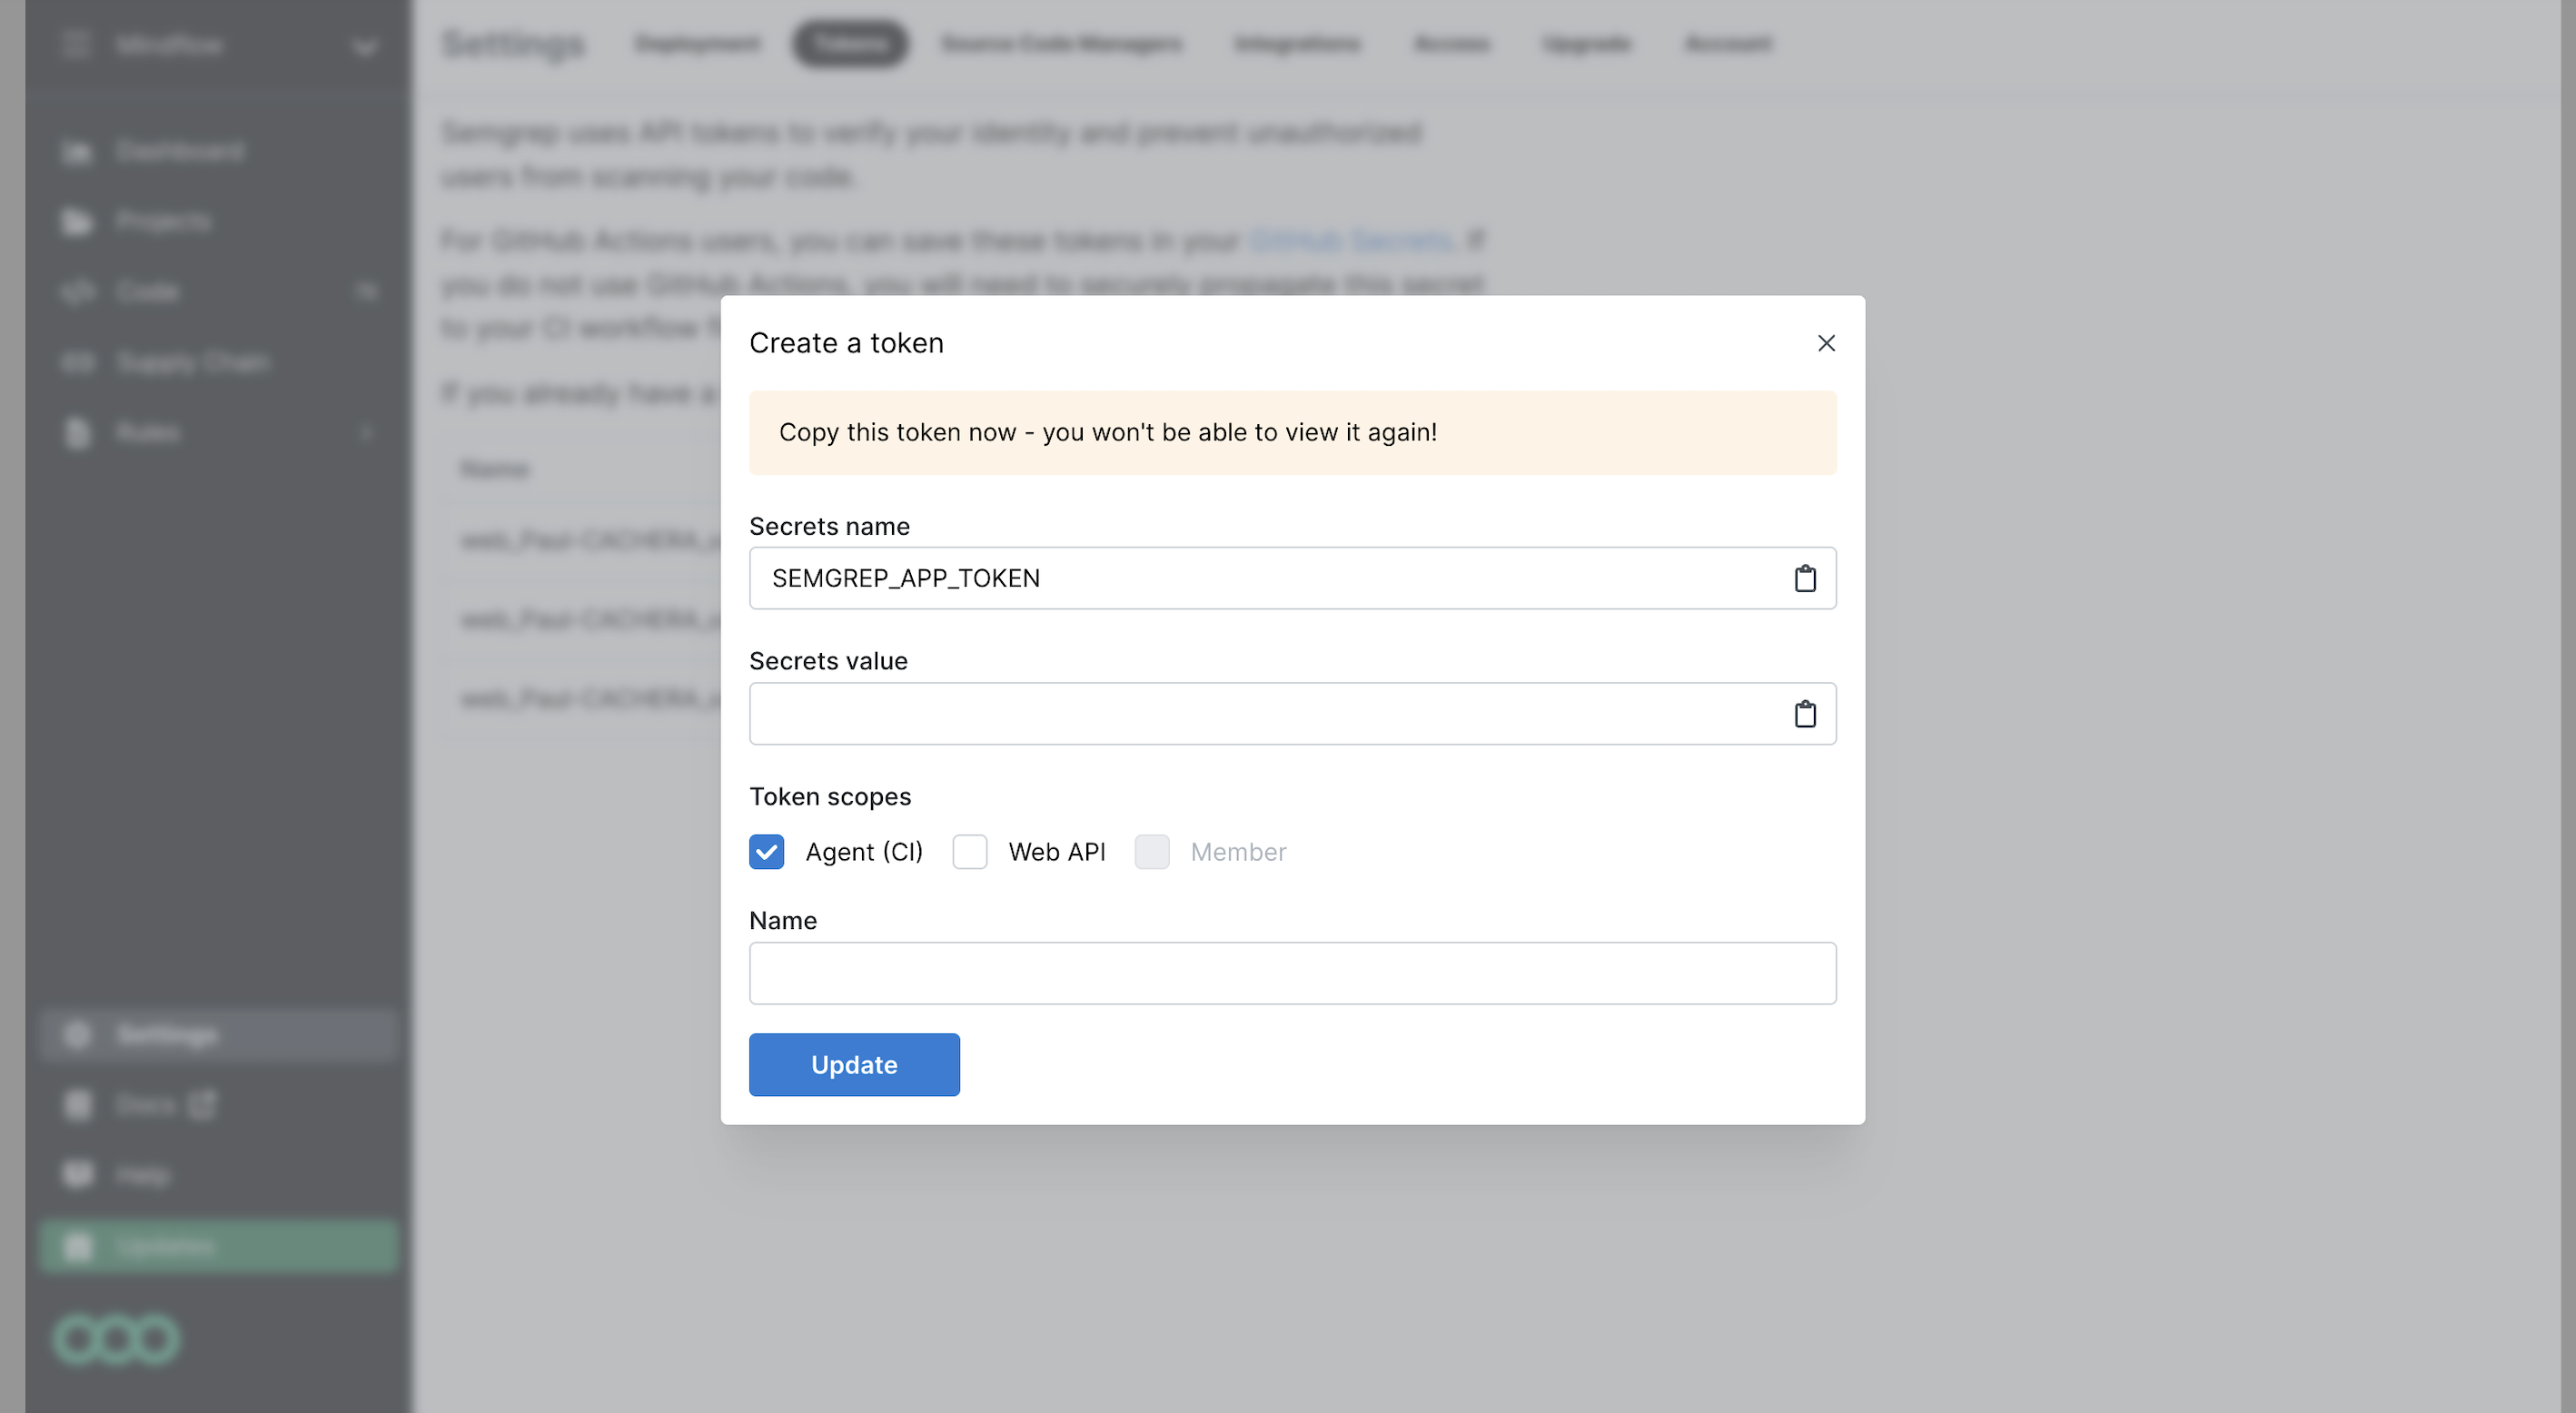
-
Click on the
+and then click on the ⚙️ in the add step menu.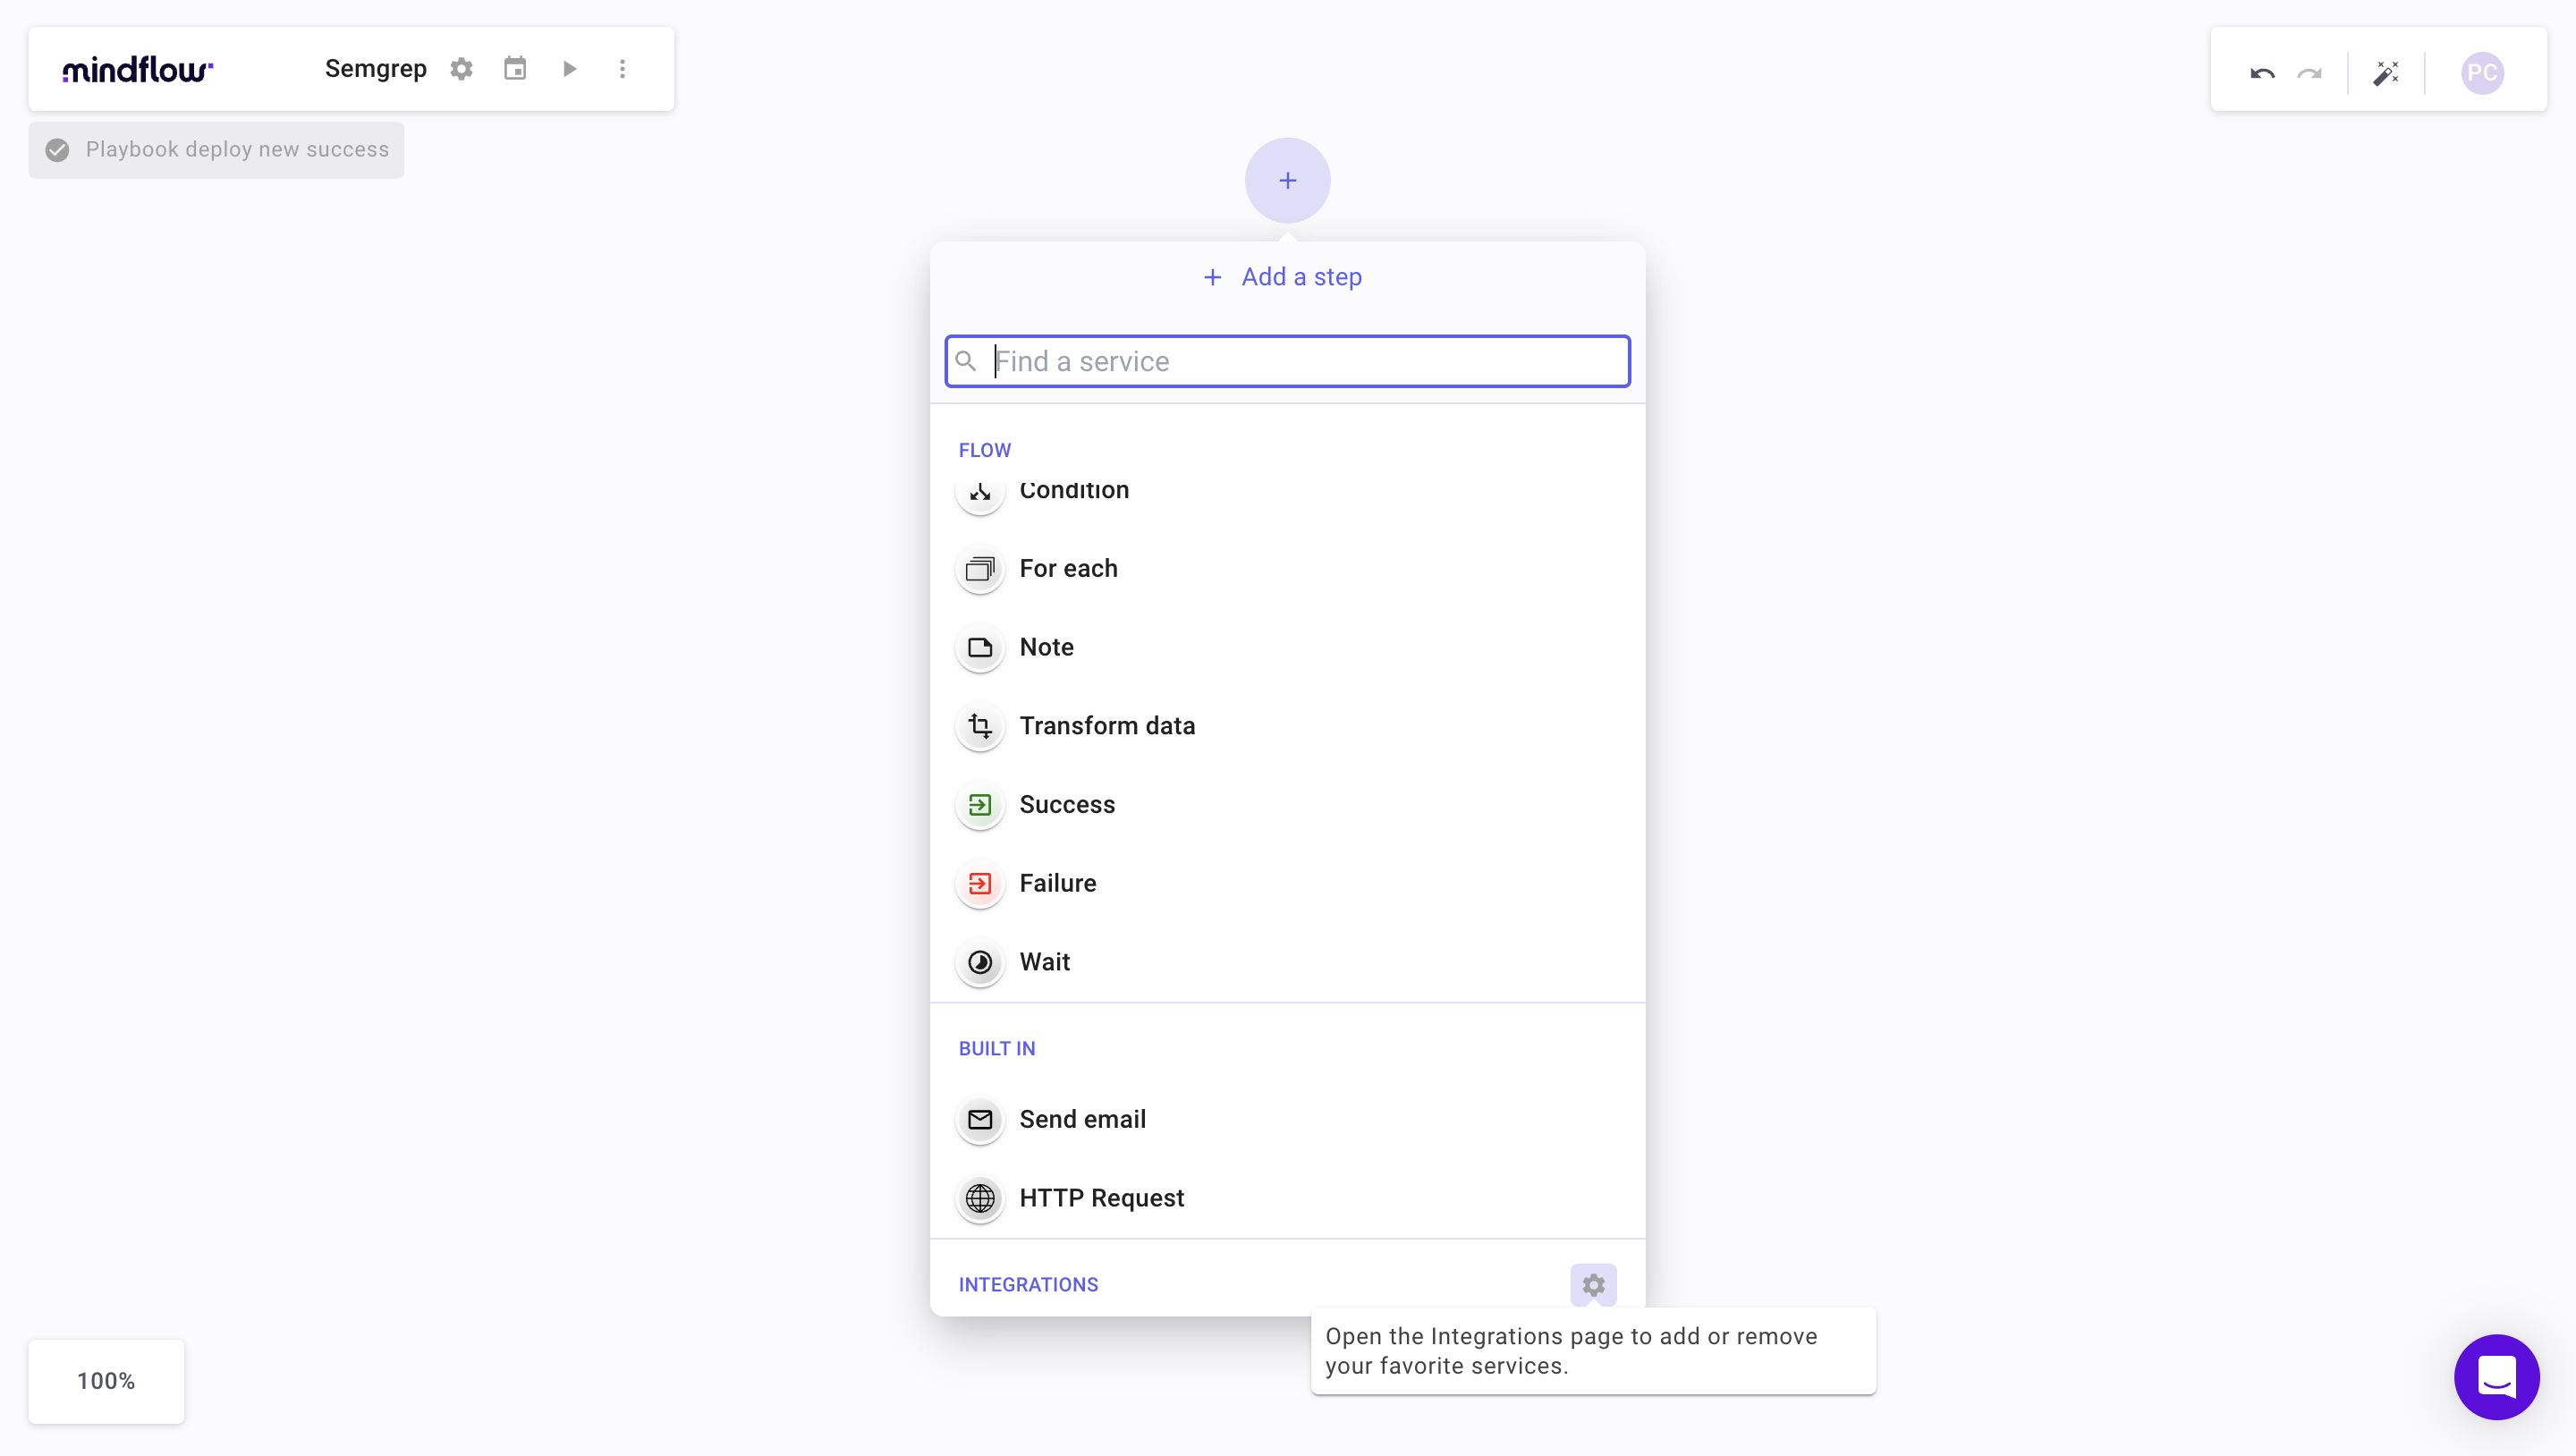
-
Search for Semgrep in the search bar, click on the first result and then click on the
+integration button.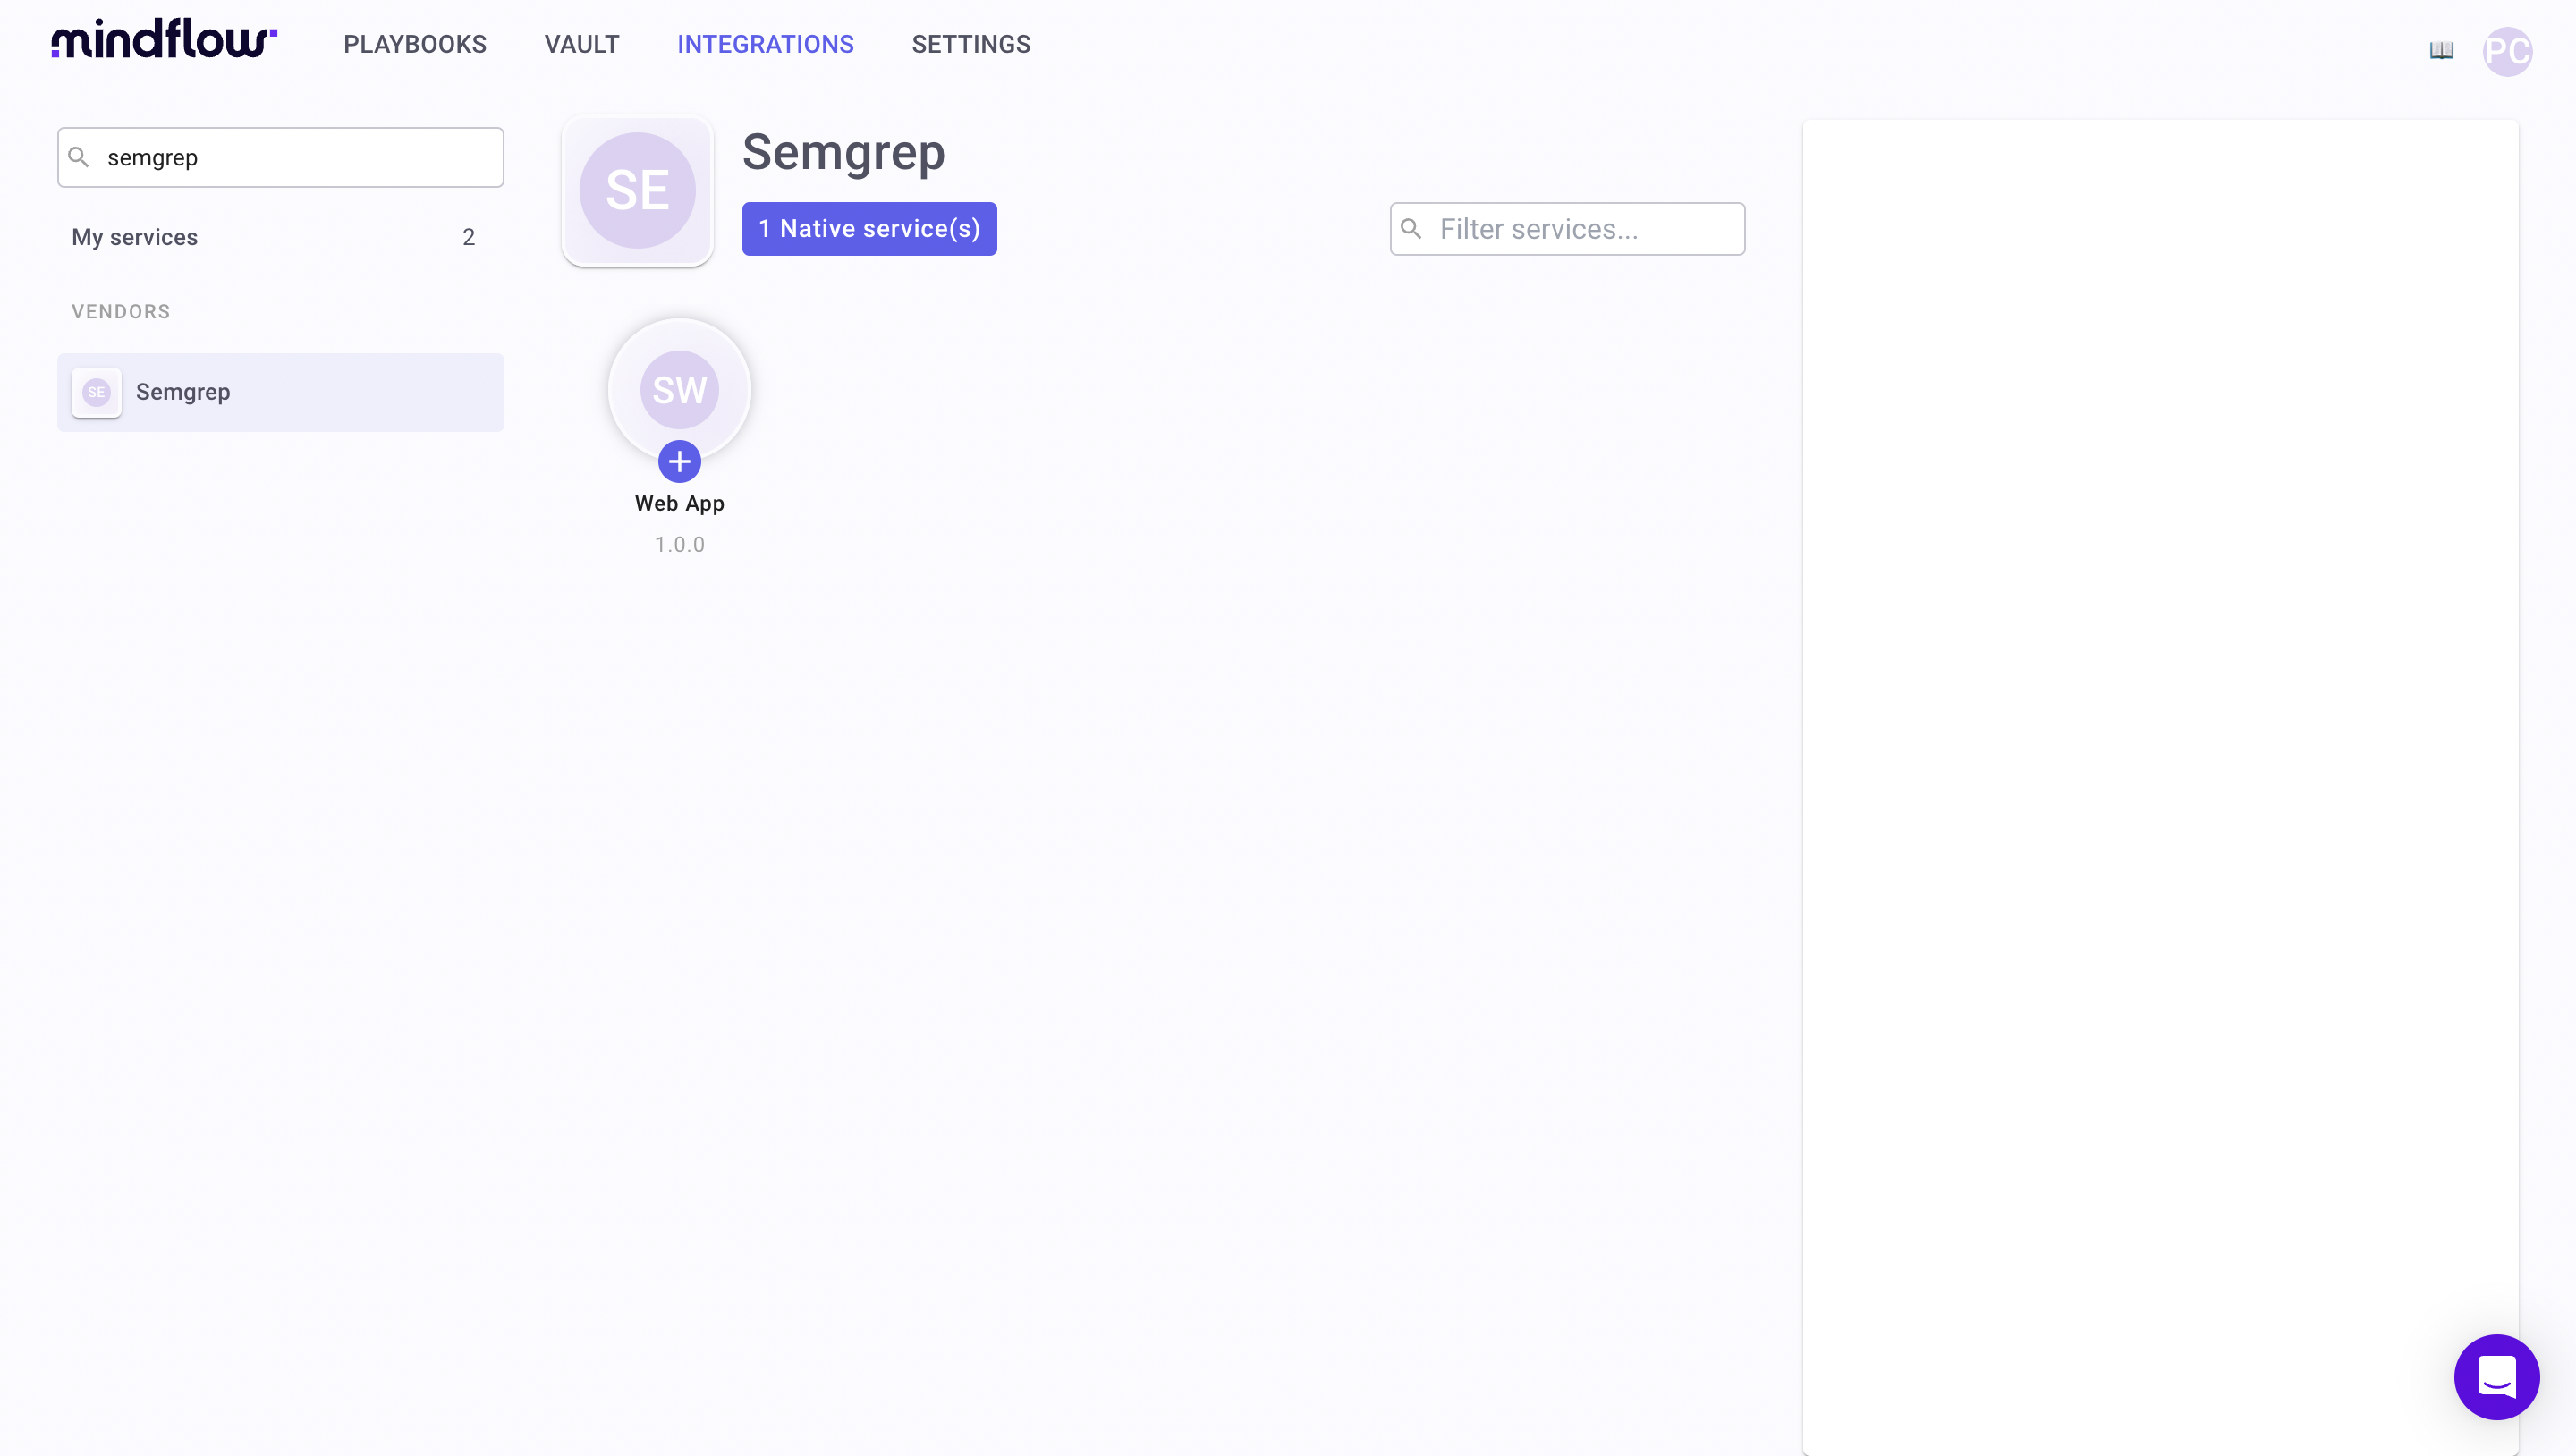
-
Click on the
+button and search for semgrep in the search bar, then select one of the following actions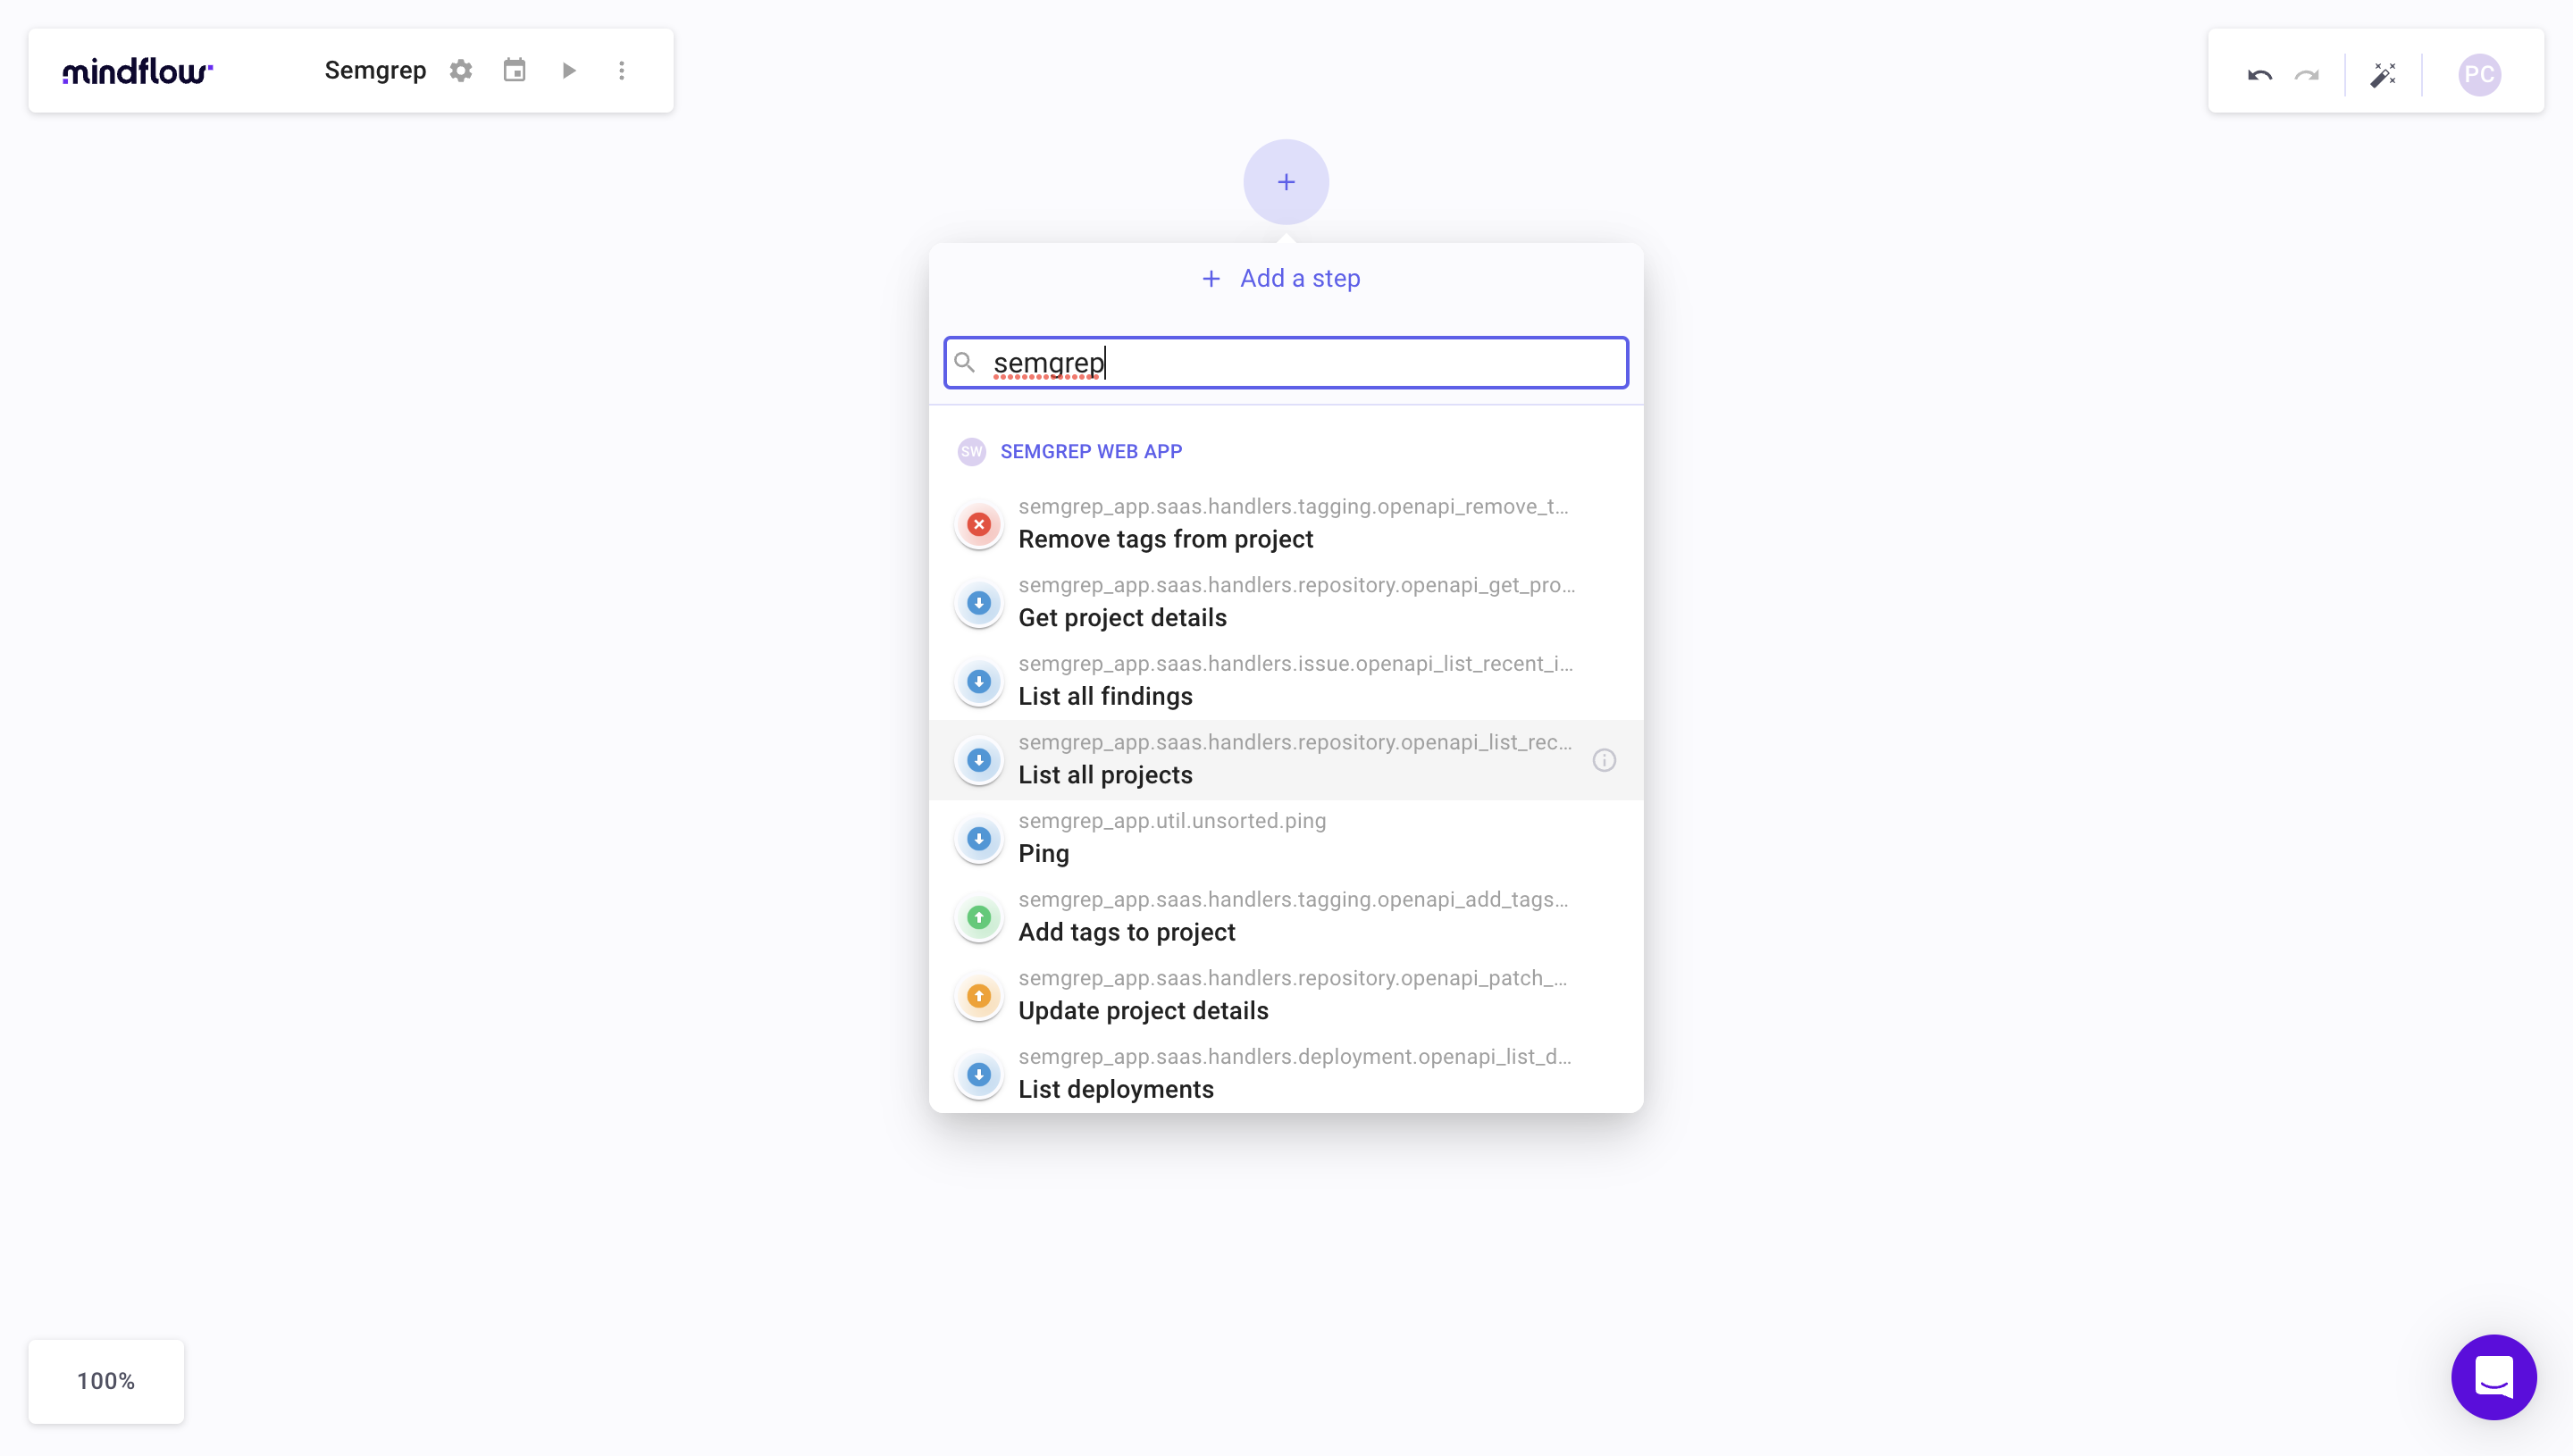
-
Fill in the mandatory fields of the input category
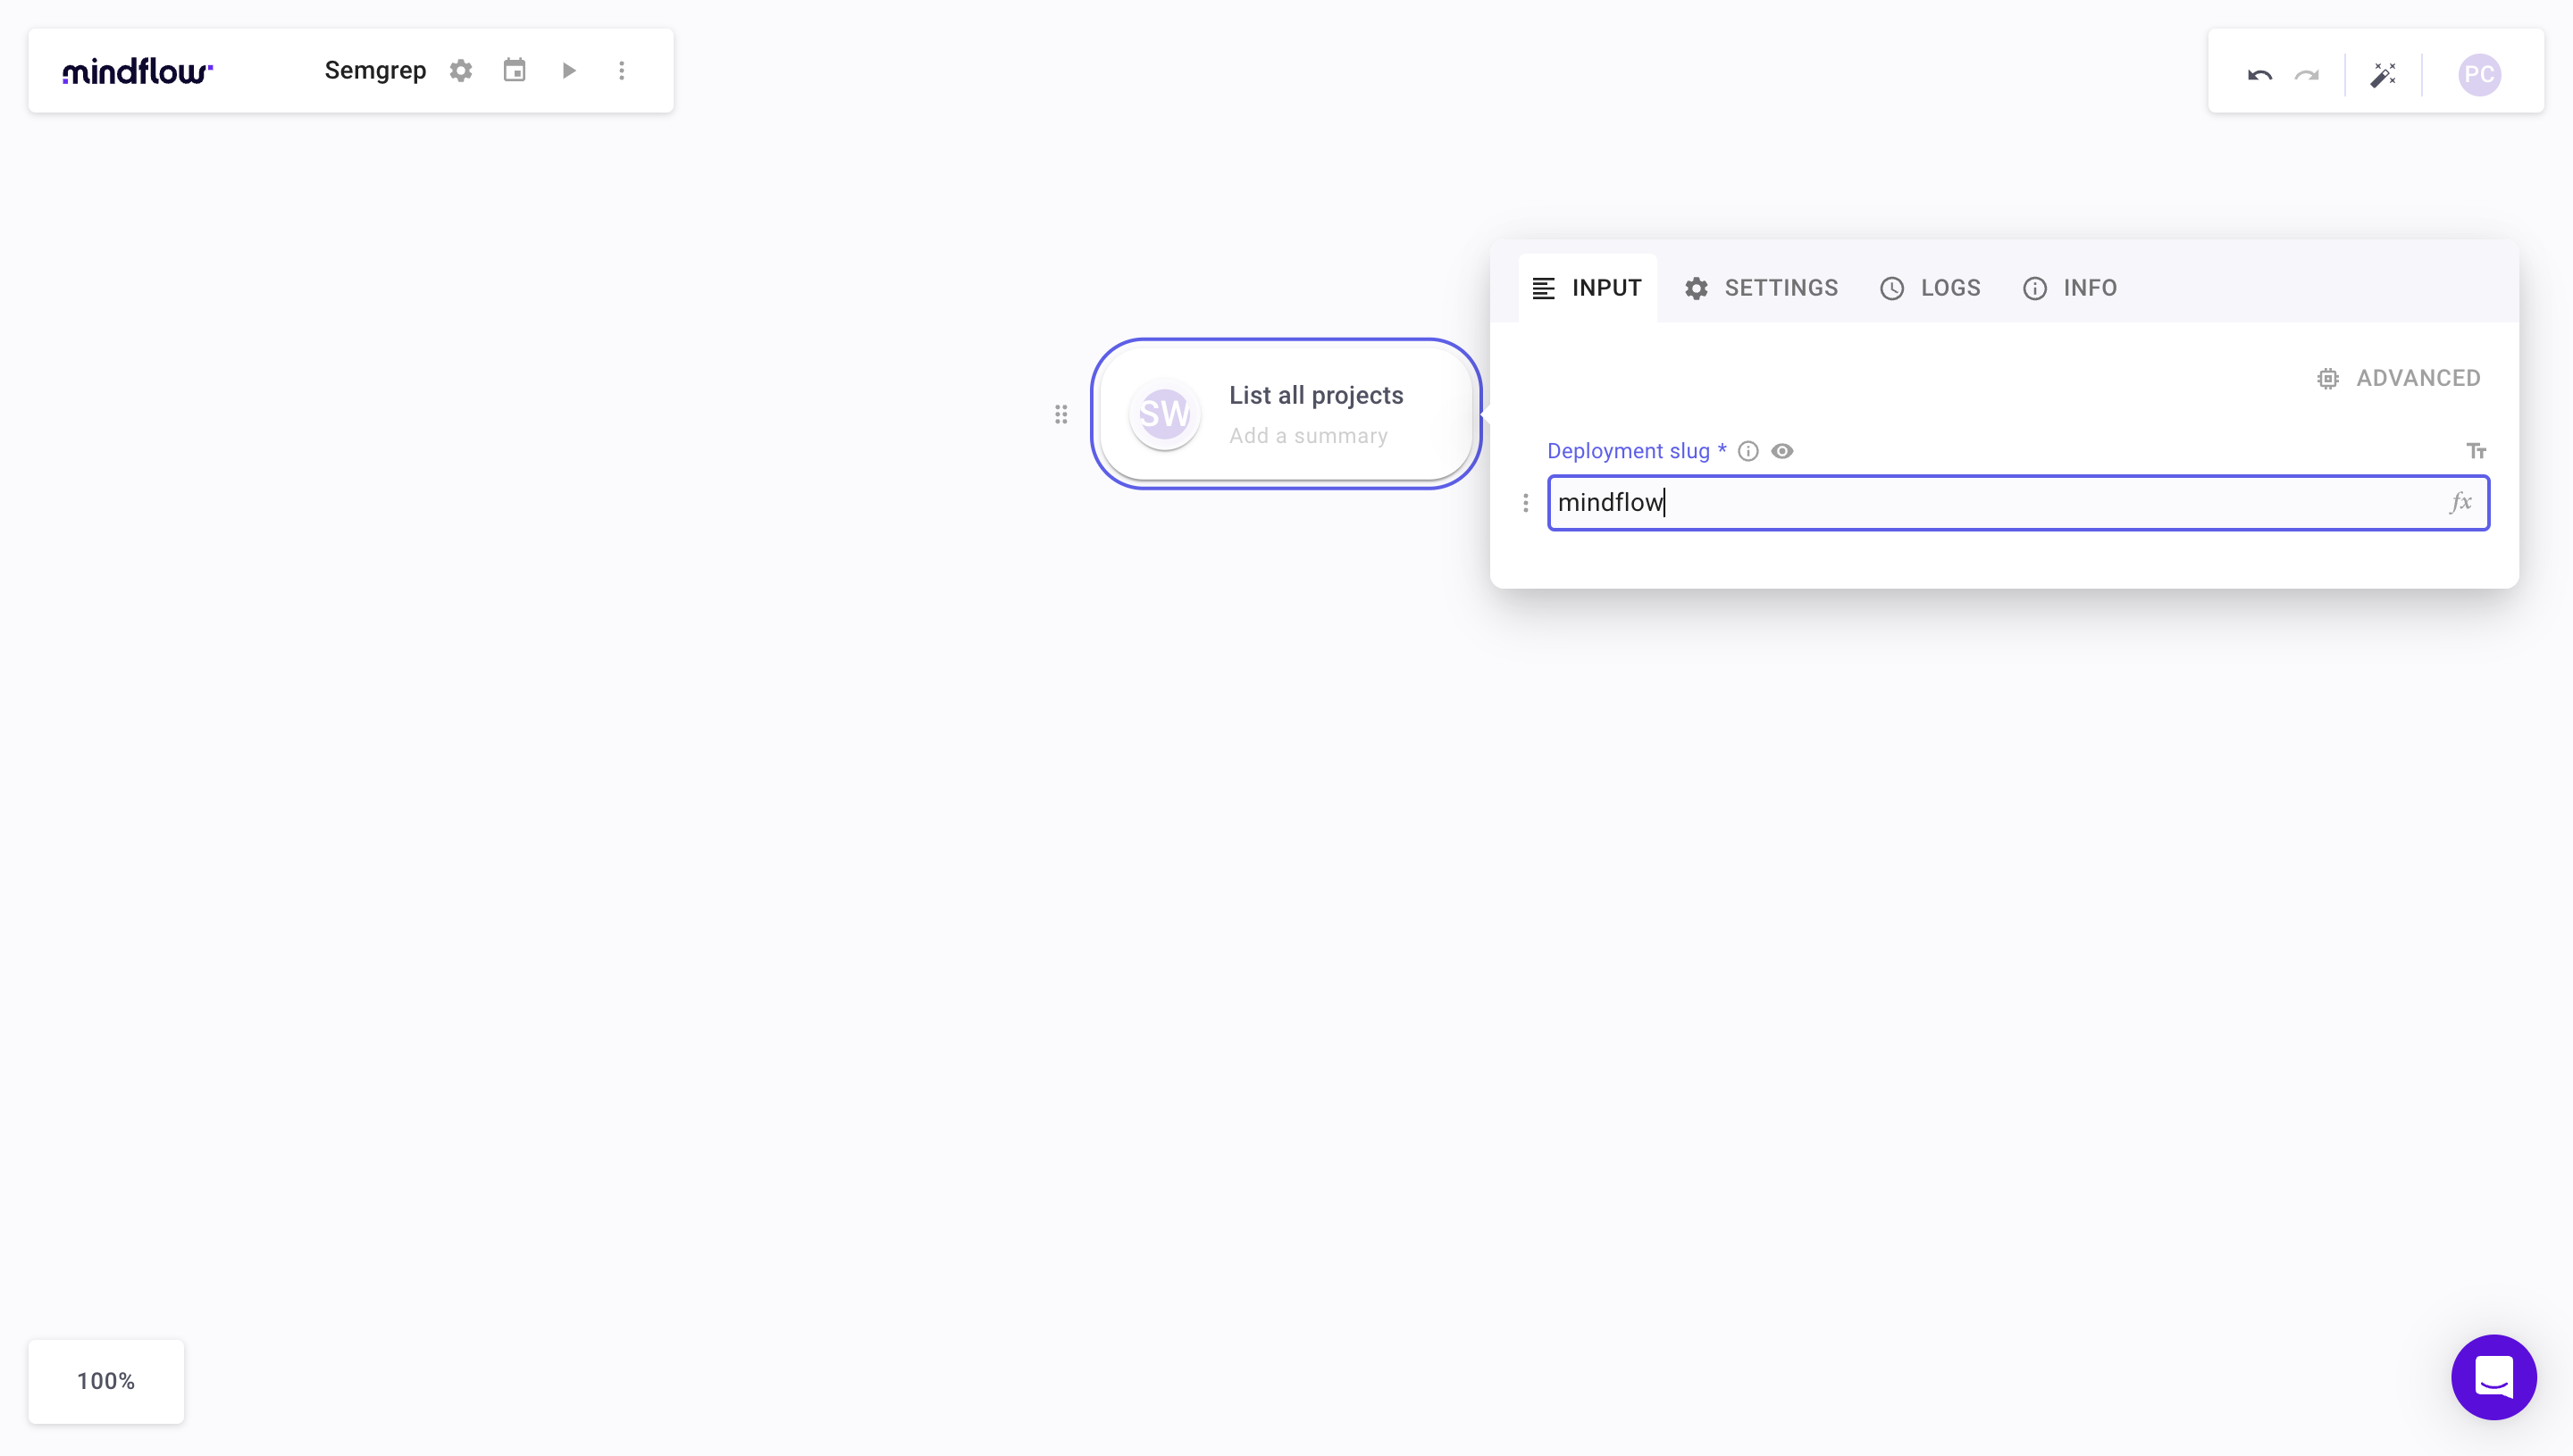
-
Go to the settings section, click in the
Credentialfield and click on theCreate a credentialbutton.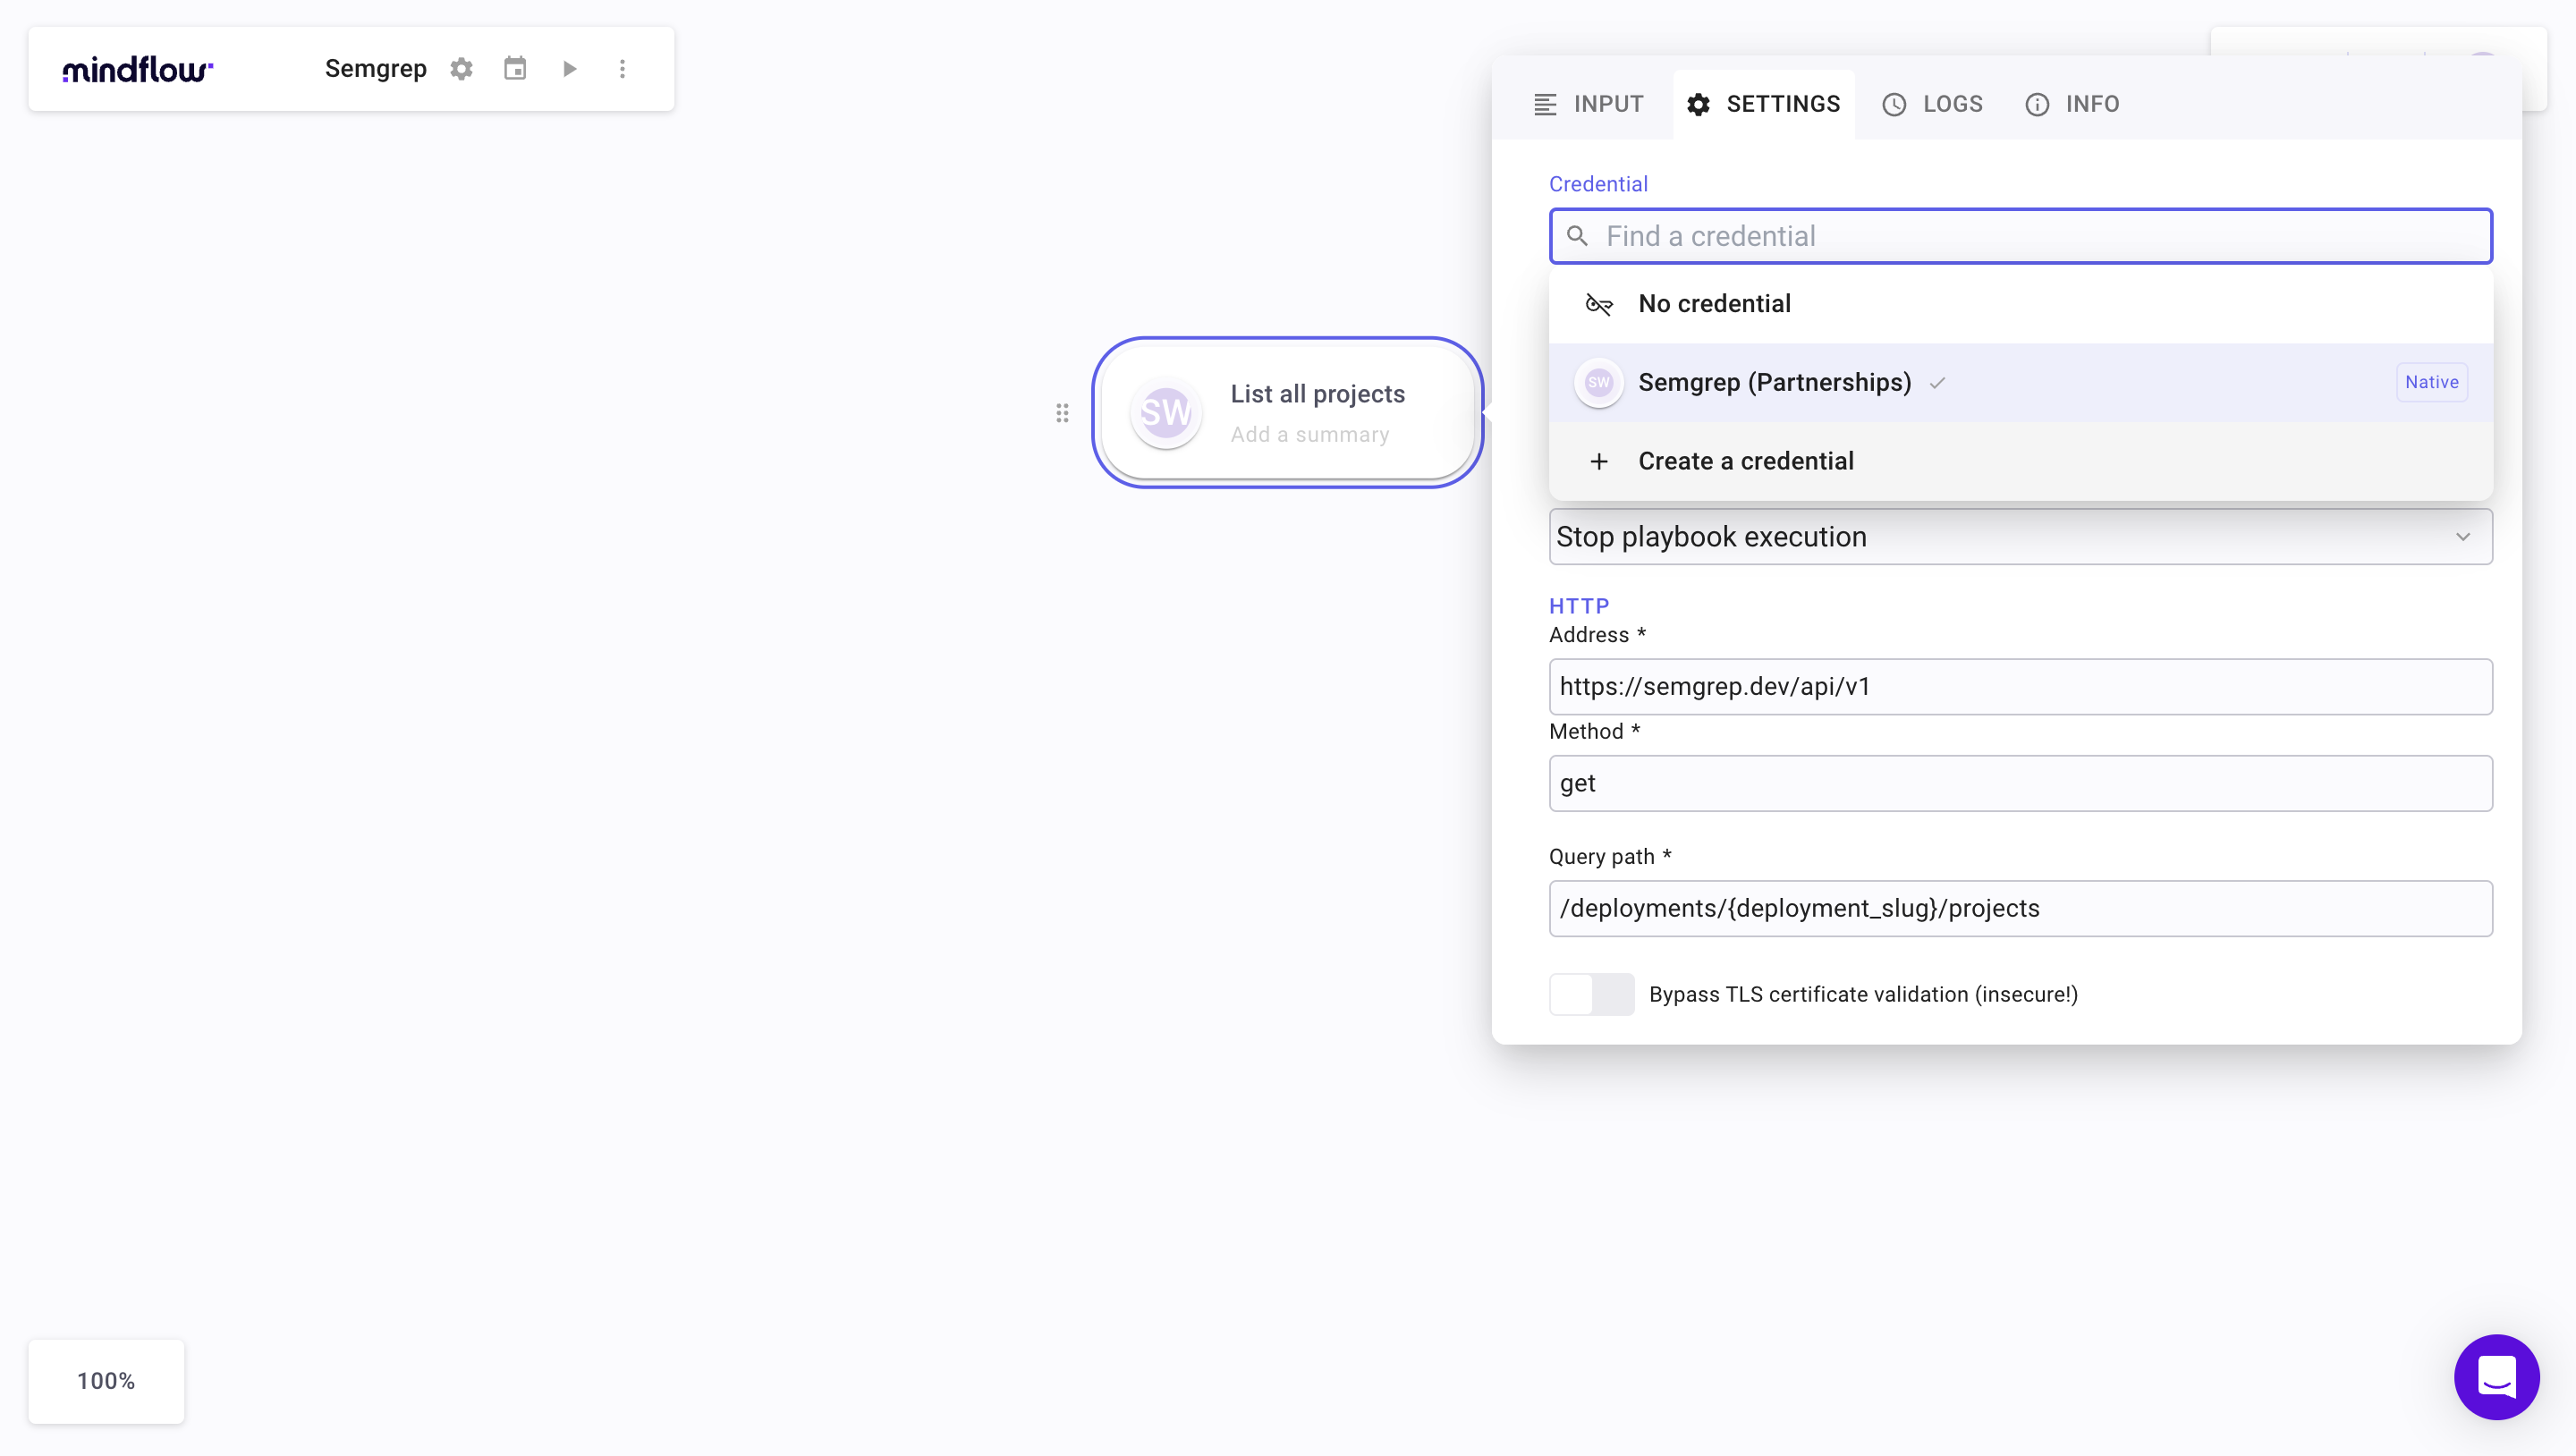
-
Select
HTTP API Keytype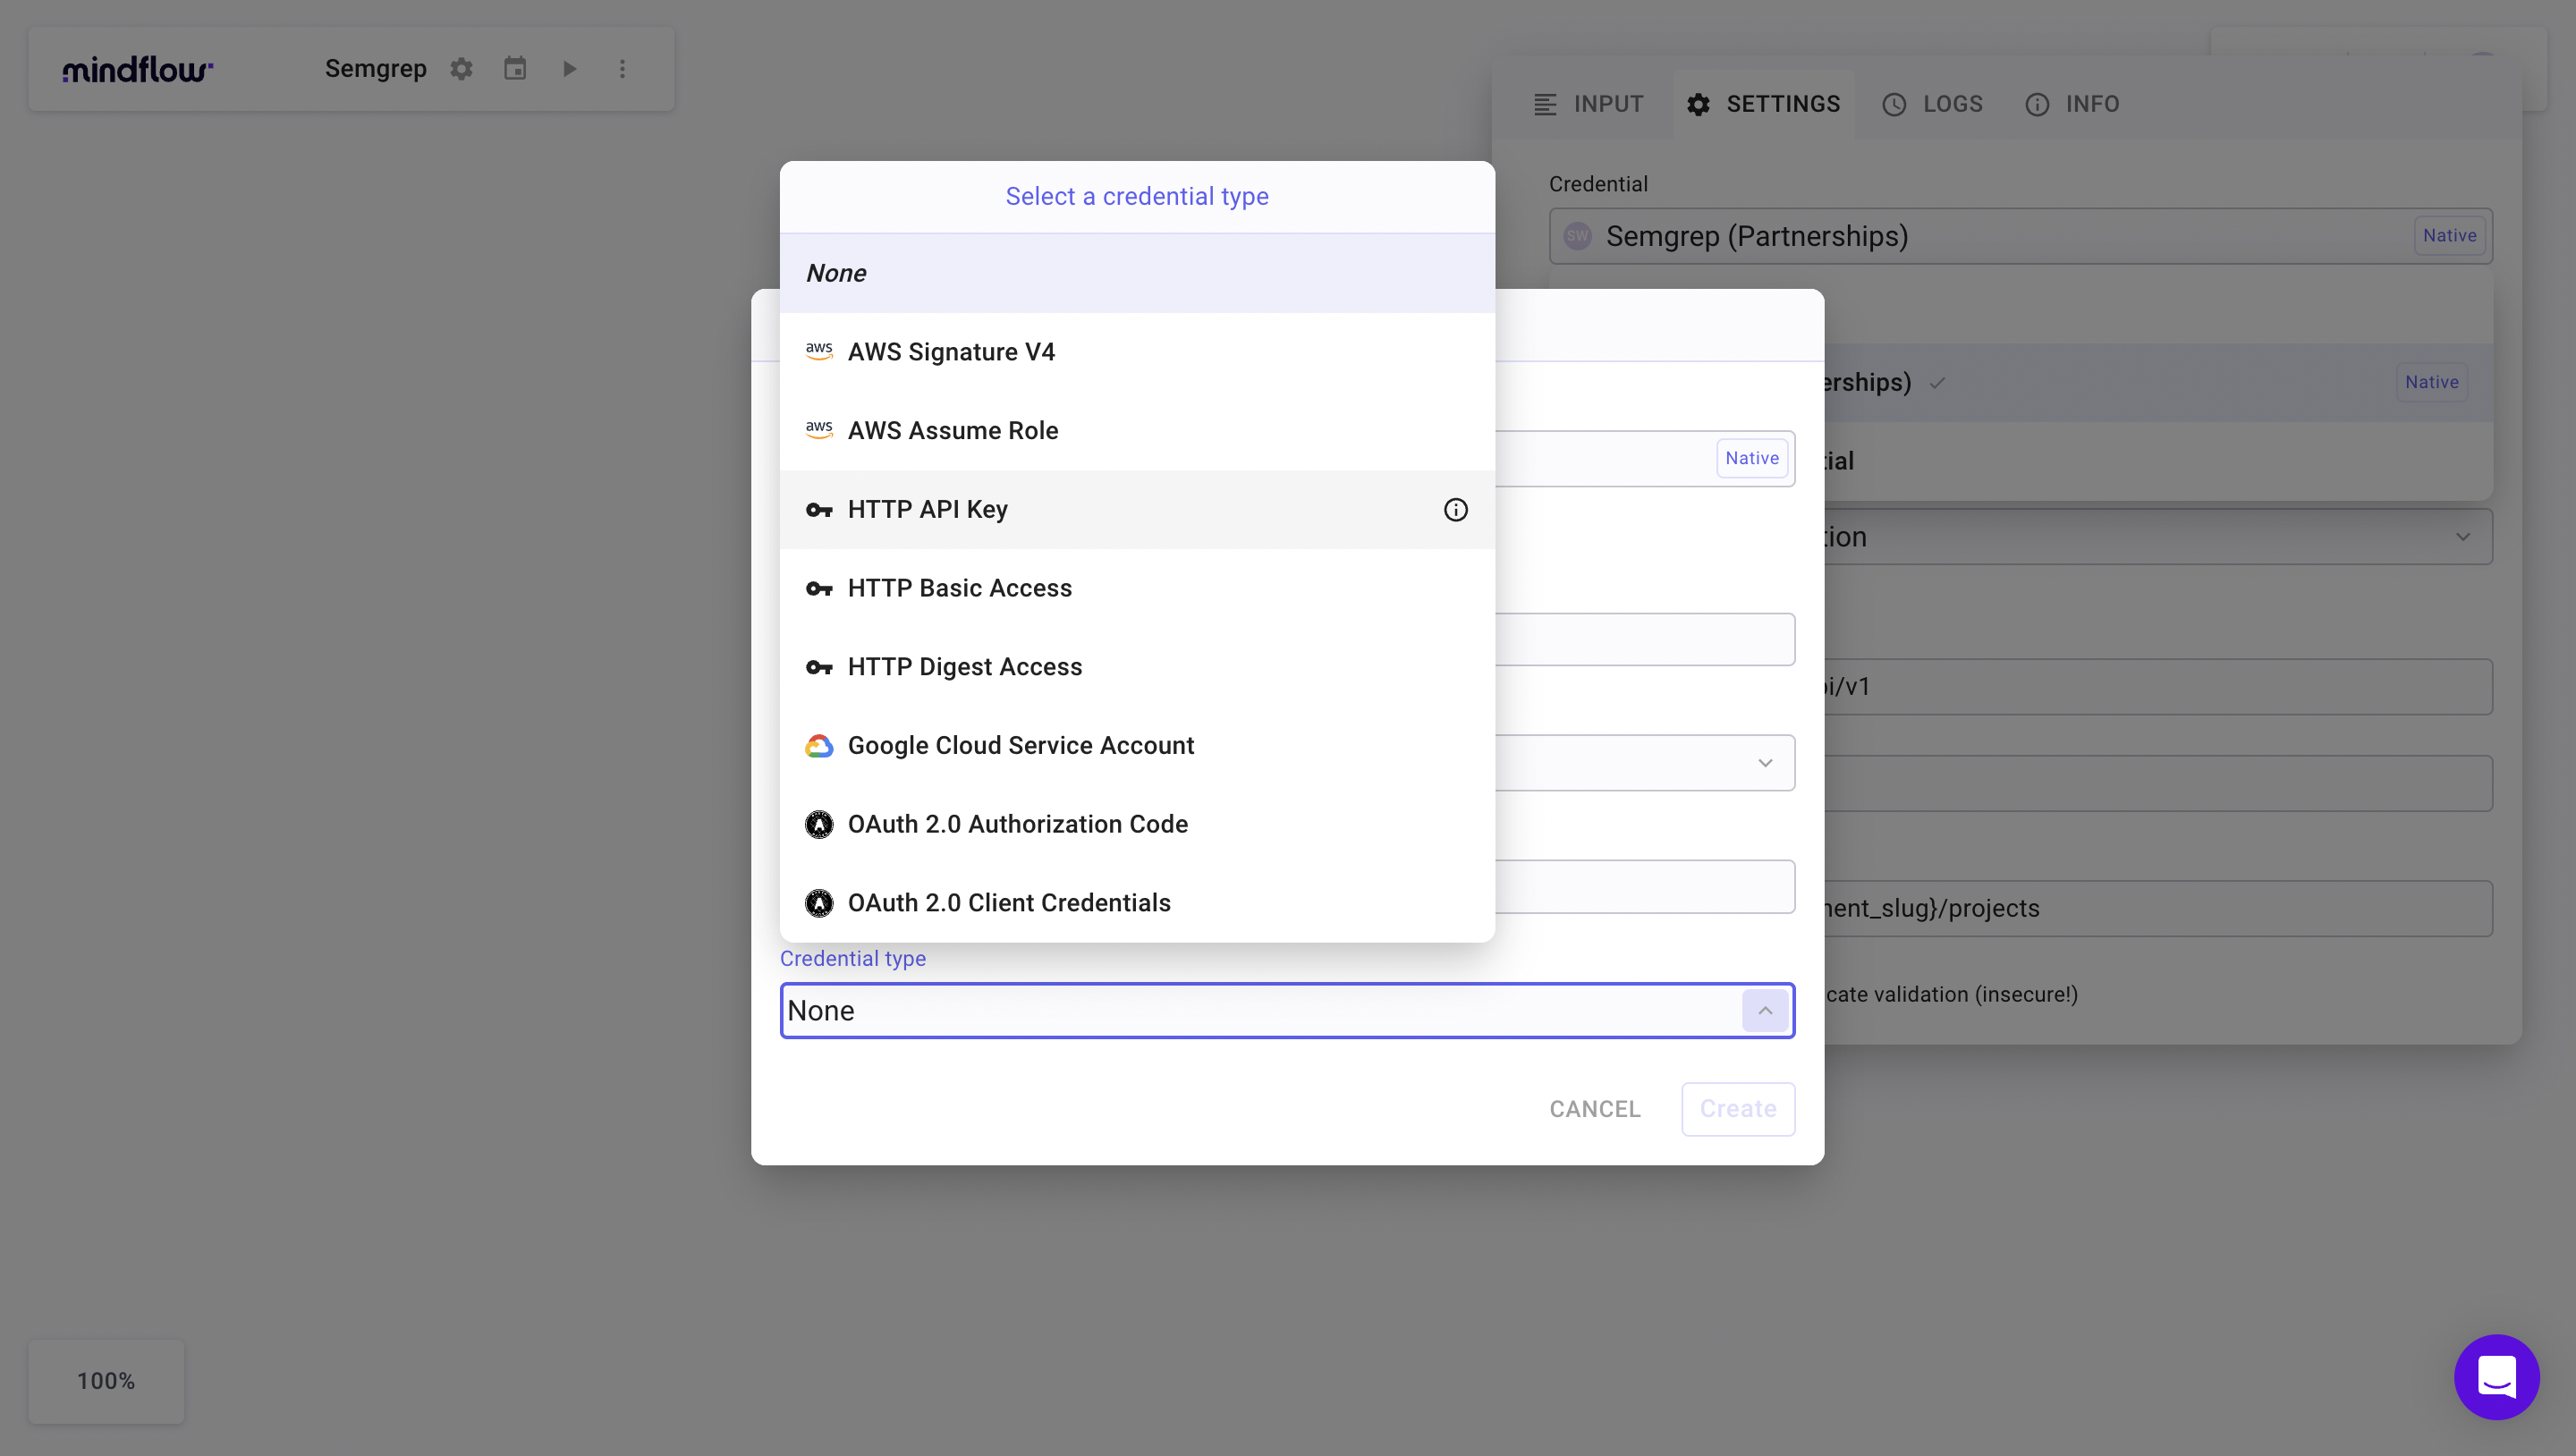
-
Insert Authorization in the
Keyfield and Bearer<YOUR_API_KEY>in theValuefield.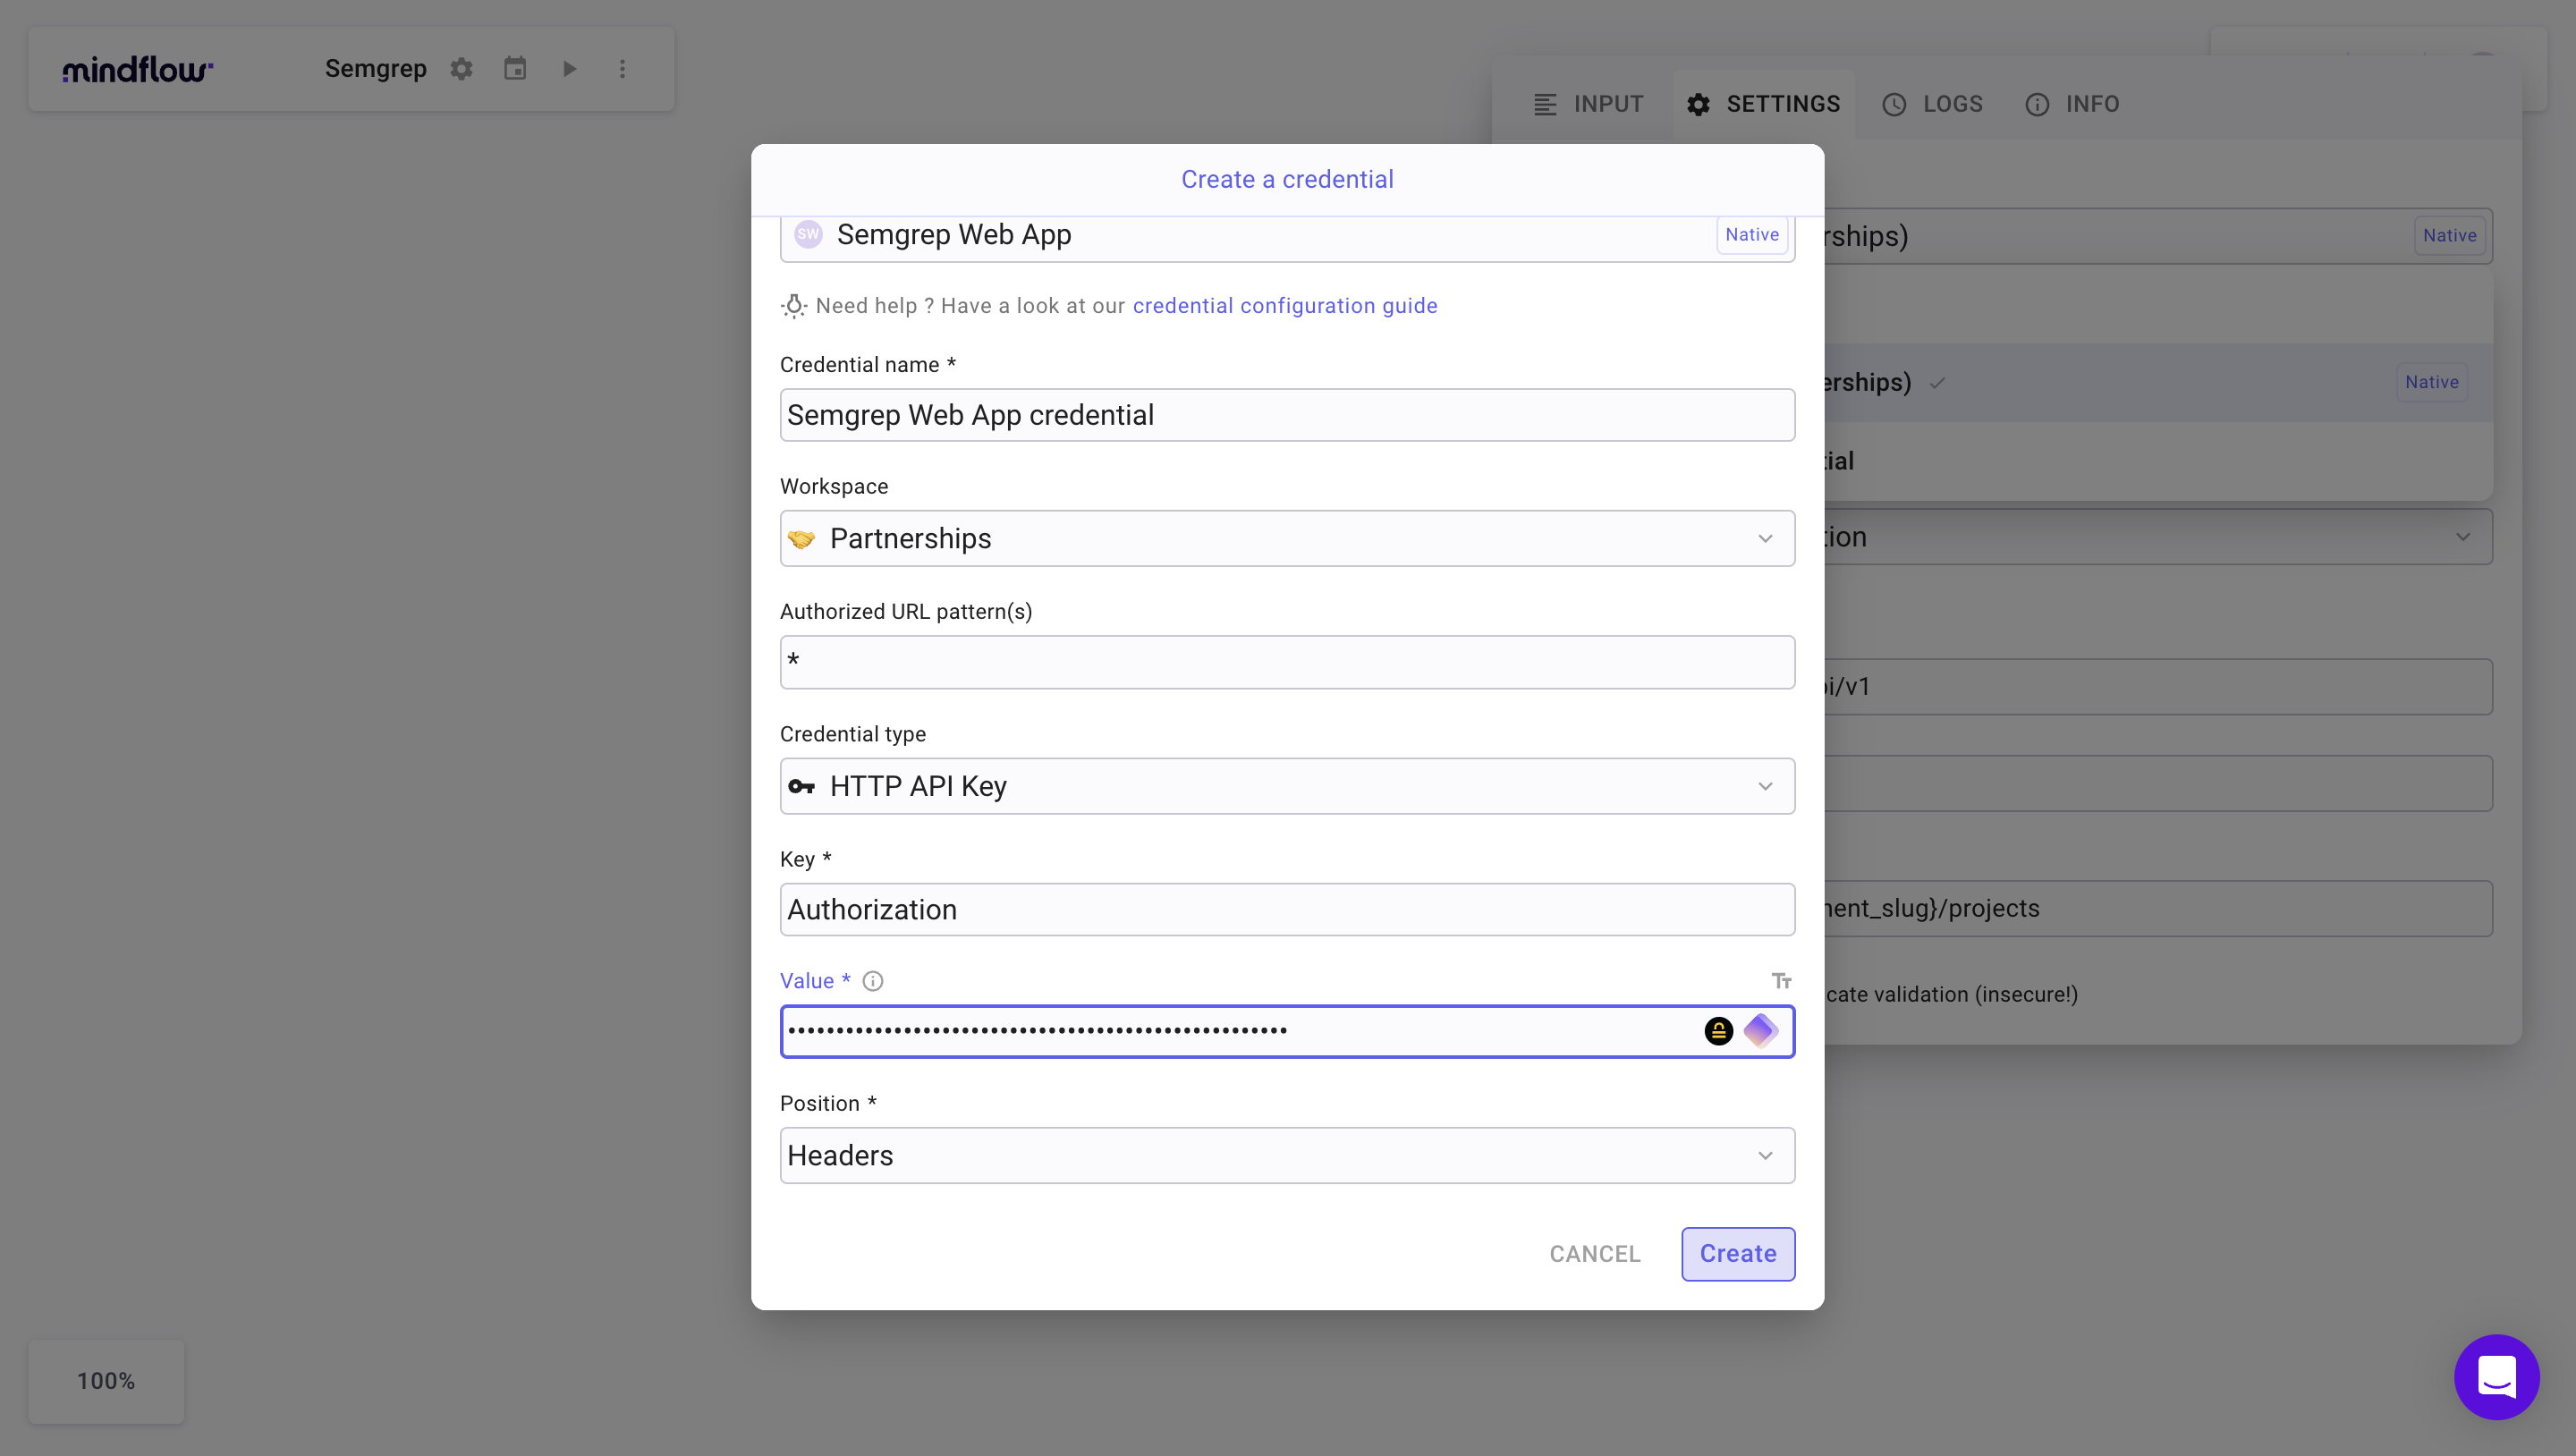
-
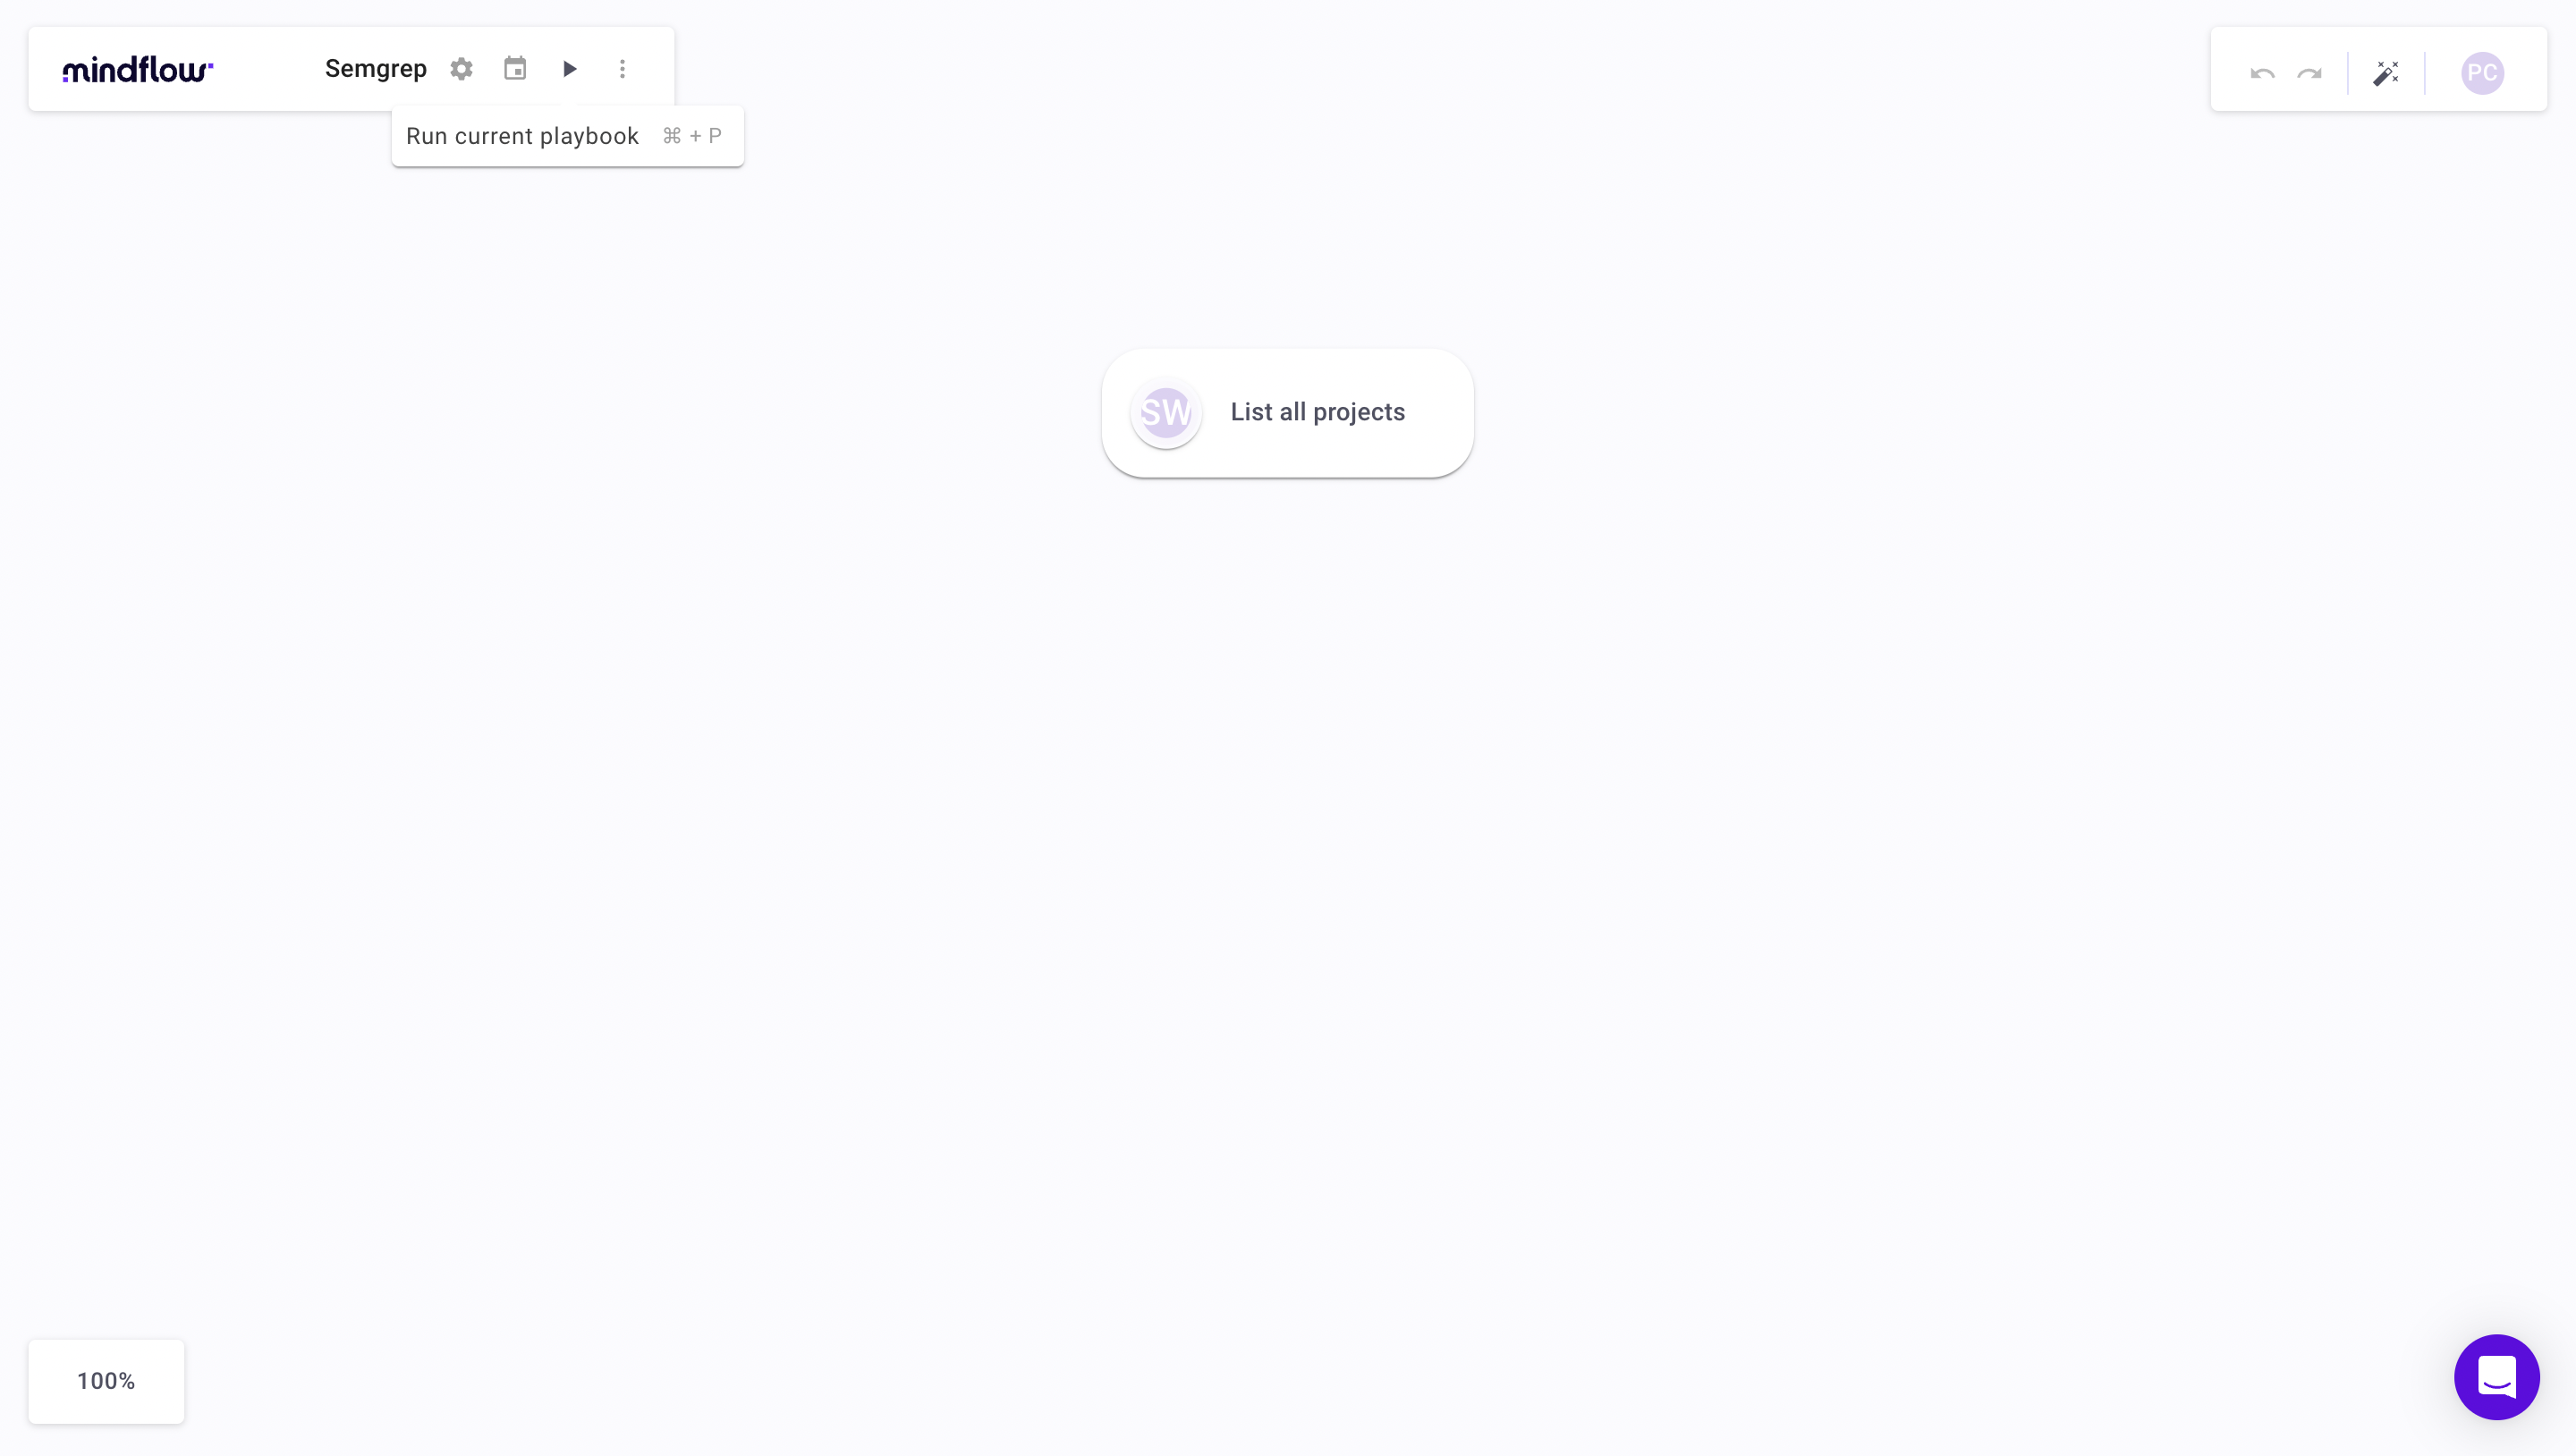
Run your flow by clicking on the ▶️ icon at top left
-
Congratulations on deploying and running your first flow with Semgrep integration 🎉